Virtual environments, like V2 Cloud, are essential for businesses today, especially with remote work on the rise. However, leaving local drives and USB devices accessible poses serious risks, making it crucial to block access to these devices. These include unauthorized data transfers, malware infections, and breaches of sensitive information.
The good news? You can disable drive and USB redirection using Group Policy in Windows. This ensures your Cloud Computer remains secure while keeping your virtual environment streamlined and focused.
Let’s explore how to protect your Cloud Computer by disabling drive and USB redirection.
IN THIS GUIDE
Why Restrict Drive and Removable Storage Devices Redirection?
Disabling Drive Redirection with Group Policy
Restricting USB Device Redirection with Group Policy
WordPress Table of Contents by Topic
Why Restrict Drive and Removable Storage Devices Redirection?
Disabling drive and USB redirection in virtual environments is vital to safeguard your data. Whether you’re managing sensitive information or protecting against malware, restricting these features reduces security risks and enhances system performance.
- Data Leakage: Users can transfer sensitive files from the virtual environment to their local devices, increasing the risk of exposure.
- Malware Infections: USB devices are a common source of malware, ransomware, and other malicious software. Unrestricted access can compromise the entire system.
- Unauthorized Access: Local drive redirection can allow users to access files and folders that shouldn’t be accessible in a secure workspace.
- Enhanced Security: Limiting access reduces the chance of breaches and unauthorized data sharing.
- Optimized Performance: By restricting unnecessary access, virtual machines operate more efficiently without the burden of handling redirected devices.
- Controlled Environment: These restrictions ensure that users focus only on resources within the virtual machine, maintaining a professional and streamlined workspace.
Disabling Drive Redirection with Group Policy
Follow these detailed steps to disable drive redirection in your virtual environment using Group Policy. This ensures users cannot access local drives (e.g., their C: drive) while connected to your Cloud Computer.
Step 1: Connect to the Cloud Computer
- Log in to your Cloud Computer as an administrator.
- Open the Windows Start Menu and type Run in the search bar.
- Under the Apps section, click on the Run option.

Step 2: Open the Group Policy Editor
- In the Run dialog box, type gpedit.msc and press Enter.
- This launches the Local Group Policy Editor, where you can modify Group Policy settings for your Cloud Computer.

Step 3: Navigate to the Policy Settings
- In the Local Group Policy Editor, expand the following folders:
- Administrative Templates
- Windows Components
- Remote Desktop Services
- Remote Desktop Session Host
- Device and Resource Redirection

Step 4: Configure the Drive Redirection Policy
- In the right-hand pane, locate the policy titled “Do not allow drive redirection.”
- Double-click the policy to open its settings window.
Step 5: Enable the Policy
- In the policy settings window, select the Enabled option.
- Click Apply and then OK to save your changes.

Step 6: Apply the Changes
- You need to update the Group Policy settings to ensure the policy is active. You can do this by:
- Opening the Command Prompt (type cmd in the Windows search bar and press Enter).
- In the Command Prompt window, type gpupdate /force and press Enter.
- For the changes to take effect for all users, restart the Cloud Computer.
Important Notes
- This policy will take effect for new remote sessions using RDP (Remote Desktop Protocol) or V2 Cloud clients. Existing sessions will need to be restarted for the policy to apply.
- By enabling this policy, all local drives and mapped network drives on the user’s machine will be hidden and inaccessible during remote desktop sessions.
- If you only want to apply this policy to specific users or groups, the Cloud Computer must be joined to Active Directory. Configure the policy under a specific Group Policy Object (GPO) for the targeted users or groups.
Restricting USB Device Redirection with Group Policy
Restricting USB device redirection is essential to prevent unauthorized file transfers and mitigate the risk of malware introduction into your virtual environment. Follow these detailed steps to block USB redirection using Group Policy in Windows.
Step 1: Open the Group Policy Management Tool
- Log in to your Cloud Computer as an administrator.
- Click the Start Menu and type Group Policy into the search bar.
- Select Edit Group Policy from the search results to launch the Local Group Policy Editor.

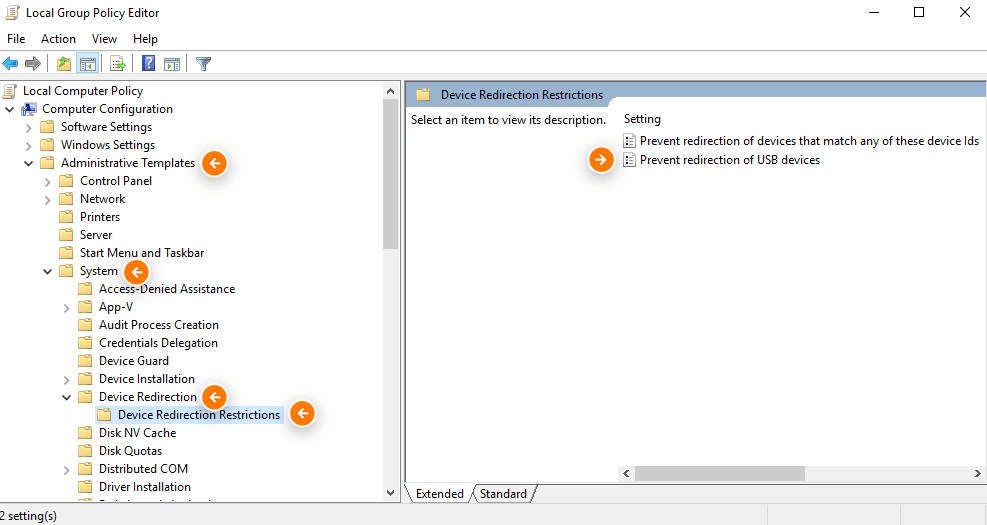
Step 2: Navigate to the USB Device Policy Settings
- In the Local Group Policy Editor, expand the following folders:
- Administrative Templates
- System
- Device Redirection
- Device Redirection Restriction
- Locate the policy labeled “Prevent Redirection of USB devices.”
Step 3: Configure the USB Device Redirection Policy
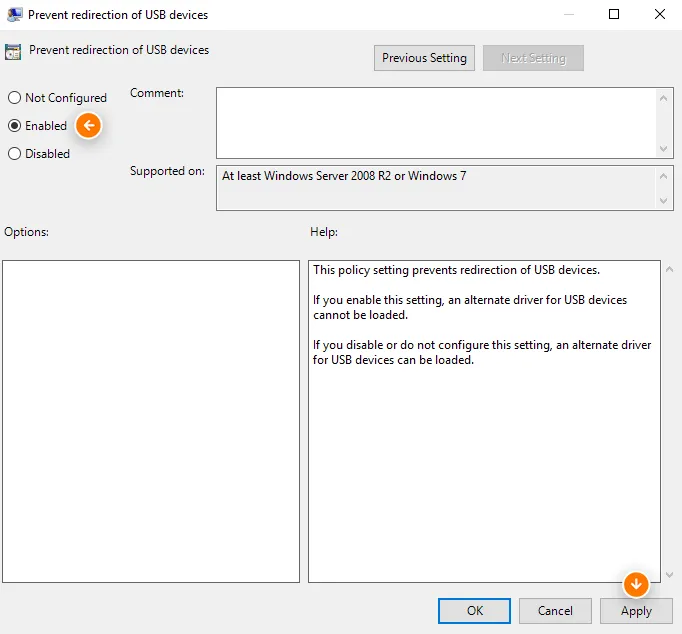
- Double-click the “Prevent Redirection of USB devices” policy to open its settings window.
- In the policy window, select the Enabled option.
- Click Apply and then OK to save your changes.
Step 4: Update Group Policy Settings
- To activate the new policy, you must update the Group Policy settings on the Cloud Computer.
- Open the Command Prompt:
- Type cmd in the Windows Search Bar and press Enter.

- In the Command Prompt window, type the following command and press Enter: gpupdate

Step 5: Reboot the Cloud Computer
- Restart your Cloud Computer to ensure the changes are applied to all users.
- The policy will block USB device redirection for all users connecting via Remote Desktop Protocol (RDP) or V2 Cloud clients.
Additional Notes
- This policy disables USB redirection for all users accessing the Cloud Computer. If you need to restrict USB access for specific users or groups, ensure your Cloud Computer is part of an Active Directory domain and configure the policy under a targeted Group Policy Object (GPO).
- USB redirection is often used for external storage devices, scanners, and input devices. Ensure users are aware of the limitations before implementing this restriction.
- If you need to apply the policy immediately for all active sessions, terminate the current sessions and have users reconnect after the policy update.
Next Steps
Restricting drive and USB device redirection is essential for maintaining a secure and controlled virtual environment. By using Group Policy, you can prevent unauthorized data transfers, reduce the risk of malware infections, and ensure your Cloud Computer is optimized for safe and efficient use.
Here’s a quick recap:
- Drive Redirection: Disabling this prevents users from accessing local drives during their virtual desktop sessions.
- USB Device Redirection: Restricting this blocks unauthorized USB device use, minimizing security risks.
- Implementation: Both policies are easy to configure through Group Policy on a Windows Server® and can be applied universally or selectively with Active Directory.
Taking these steps ensures your V2 Cloud setup remains secure, scalable, and aligned with modern security standards.
- Apply These Policies Today: Secure your virtual desktops by implementing the steps outlined above.
- Learn More: Check out the V2 Cloud documentation for additional tutorials and advanced configurations.
- Get Support: Need help setting up Group Policy or managing your virtual environment? Contact V2 Cloud’s support team for expert assistance.
By proactively securing your virtual environment, you’re building a foundation for safer, smarter, and more reliable cloud computing. Don’t wait—Talk to a Cloud Expert Now!




