How to Block Websites and Allow Specific Ones Using Group Policy - V2 Cloud

How to Block Websites and Allow Specific Ones Using Group Policy

July 30, 2026

Summarize: ChatGPT Perplexity

Blocking websites is a powerful way to control internet access, enhance productivity, and protect against potential security threats.

Whether you’re managing a business network, school environment, or personal device, limiting access to only a few authorized websites can help maintain focus and prevent distractions.

In this tutorial, we’ll walk you through how to block all websites except specific ones using Group Policy in a Windows Server environment. This approach is especially useful for administrators who need to enforce consistent browsing rules for multiple users.

Let’s get started!

IN THIS GUIDE

Why Block Websites on a Computer Network?

Prerequisites for Blocking Websites Using Group Policy

Step-by-Step Guide to Block Websites and Authorize Specific Ones

Apply Restrictions to All Users via Group Policy

Simplify Website Restrictions & User Management with V2 Cloud


WordPress Table of Contents by Topic


Why Block Websites on a Computer Network?

Blocking websites is a key strategy for maintaining focus, security, and compliance in any networked environment. By restricting access to non-essential or harmful websites, you can create a more controlled online experience for users.

For businesses, website blocking reduces distractions, boosting employee productivity. Studies show that employees spend over 2 hours daily on non-work-related websites. Restricting internet access to essential sites ensures time is spent on critical tasks.

In schools, limiting internet access helps prevent exposure to inappropriate or distracting content, ensuring students focus on learning. Website blocking also safeguards younger users from phishing attacks or malware threats, which often target unsuspecting visitors.

For personal use, blocking websites can reduce screen time or help maintain better digital habits. It’s also a security tool, as certain websites may carry risks like malware or phishing.

When to implement website blocking:

  • Managing productivity in the workplace.
  • Ensuring compliance with company or institution policies.
  • Enhancing security by limiting access to malicious or distracting sites.

Prerequisites for Blocking Websites Using Group Policy

Before you begin blocking websites and allowing specific ones, ensure you have the following prerequisites in place. These requirements are essential for setting up Group Policy and implementing website restrictions effectively.

1. Windows Server with Group Policy Management Enabled

Group Policy is a feature available in Windows Server environments. Ensure that the Group Policy Management Console (GPMC) is installed and accessible.

How to Check:

  • Open the Start Menu and type Group Policy Management.
  • If the console is listed, you’re ready to proceed. If not, you may need to install it via the Windows Server Manager by adding the “Group Policy Management" feature.

Tip: Make sure you have administrative privileges on the server to access and configure Group Policy settings.

2. Administrator Access to the Network

To configure website restrictions for multiple users, you’ll need admin-level permissions on the network. These permissions allow you to apply Group Policy settings across different users or devices.

Ensure the Following:

  • You have credentials for the domain administrator account.
  • You can access the server remotely if necessary.

3. User Groups Defined in Active Directory

Group Policy is most effective when applied to well-organized user groups. Use Active Directory to create or verify groups of users who will receive the policy settings.

Steps to Check or Create Groups:

  1. Open Active Directory Users and Computers on your server.
  2. Navigate to the Users folder.
  3. Right-click to create or modify groups as needed.

Example: Create a group called “Restricted Web Access" for users requiring website restrictions.

4. A List of Authorized Websites

Decide in advance which websites users should be allowed to access. Prepare a list with URLs formatted correctly (e.g., www.example.com and example.com) for use in the LAN proxy settings. Nevertheless, using a reliable proxy service here can help enforce these restrictions, ensuring that only approved websites are accessible while preventing unauthorized browsing. When validating how websites behave from external networks or different regions, administrators may also test using 4G rotating proxies to simulate real mobile connections and verify that access policies work as intended.

Pro Tip: Include only secure and necessary websites to minimize distractions or risks.

5. Local User Access for Testing

To test the configuration, you’ll need access to a local user account affected by the Group Policy settings. Testing ensures the policy applies as expected before deploying it broadly.

Steps to Test:

  1. Log into a workstation connected to the network.
  2. Verify that the restricted settings are applied after the policy is updated.

Step-by-Step Guide to Block Websites and Authorize Specific Ones

This section provides a detailed, step-by-step process to block all websites and allow access to only specific ones using Group Policy in a Windows Server environment.

Follow these instructions carefully to ensure a successful configuration.

Step 1: Open the Control Panel

  1. Right-click the Start Menu on your desktop.
  2. From the dropdown menu, select Control Panel.

Background Image

Tips:

  • If you don’t see Control Panel in the menu, type “Control Panel" in the search bar.
  • Ensure you have admin privileges on the computer to proceed.

Step 2: Access Internet Options

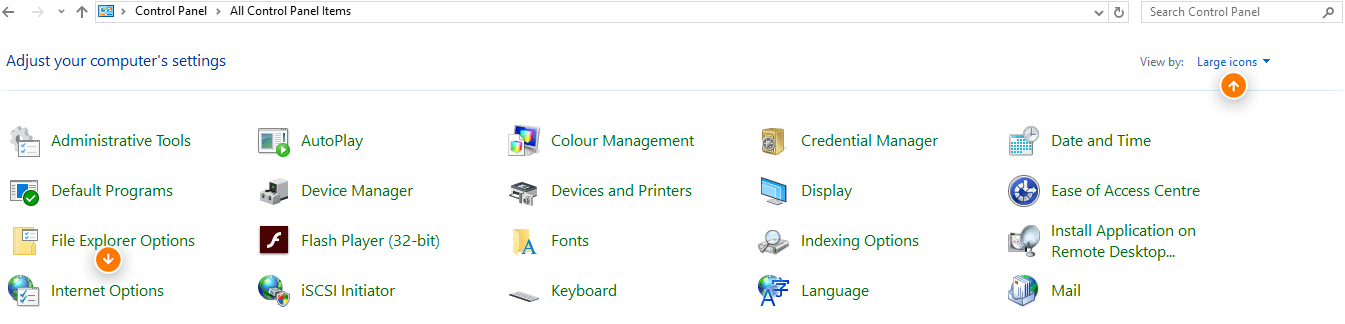
  1. In the Control Panel window, locate the View by dropdown at the top-right corner.
  2. Change it to Large icons for easier navigation.
  3. Click on Internet Options to open the settings.Background Image

Step 3: Configure LAN Settings

  1. In the Internet Options window, go to the Connections tab.
  2. Click on the LAN settings button located at the bottom.Background Image

What This Does:
This step allows you to control how the computer connects to the internet through a local area network (LAN).
Step 4: Enable Proxy Server for LAN

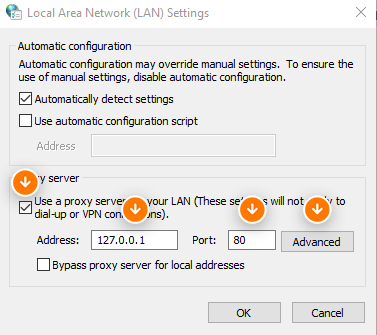
  1. In the LAN Settings window, locate the Proxy server section.
  2. Check the box next to Use a proxy server for your LAN.
  3. Enter 127.0.0.1 in the Address field.
  4. Set the Port to 80.Background Image

Why This Matters:

  • Using 127.0.0.1 (localhost) as the proxy effectively blocks access to all websites.
  • The next step will configure exceptions to allow access only to specific websites.

Step 5: Add Exceptions for Allowed Websites

  1. Click the Advanced button next to the proxy settings.
  2. In the Proxy Settings window, go to the Exceptions section under “Do not use proxy server for addresses beginning with."
  3. Enter the URLs of websites you want to allow. For example:

Important Notes:

  • Separate each website address with a semicolon (e.g., www.youtube.com;youtube.com).
  • Include variations of the website address (with and without “www") to ensure proper access.
  1. Once you’ve added all the desired websites, click OK to save your settings and close the window.

Step 6: Apply the Settings to Group Policy

Now that the LAN settings are configured on one machine, you can replicate them across users using Group Policy:
  1. Open the Group Policy Management Console on your Windows Server.
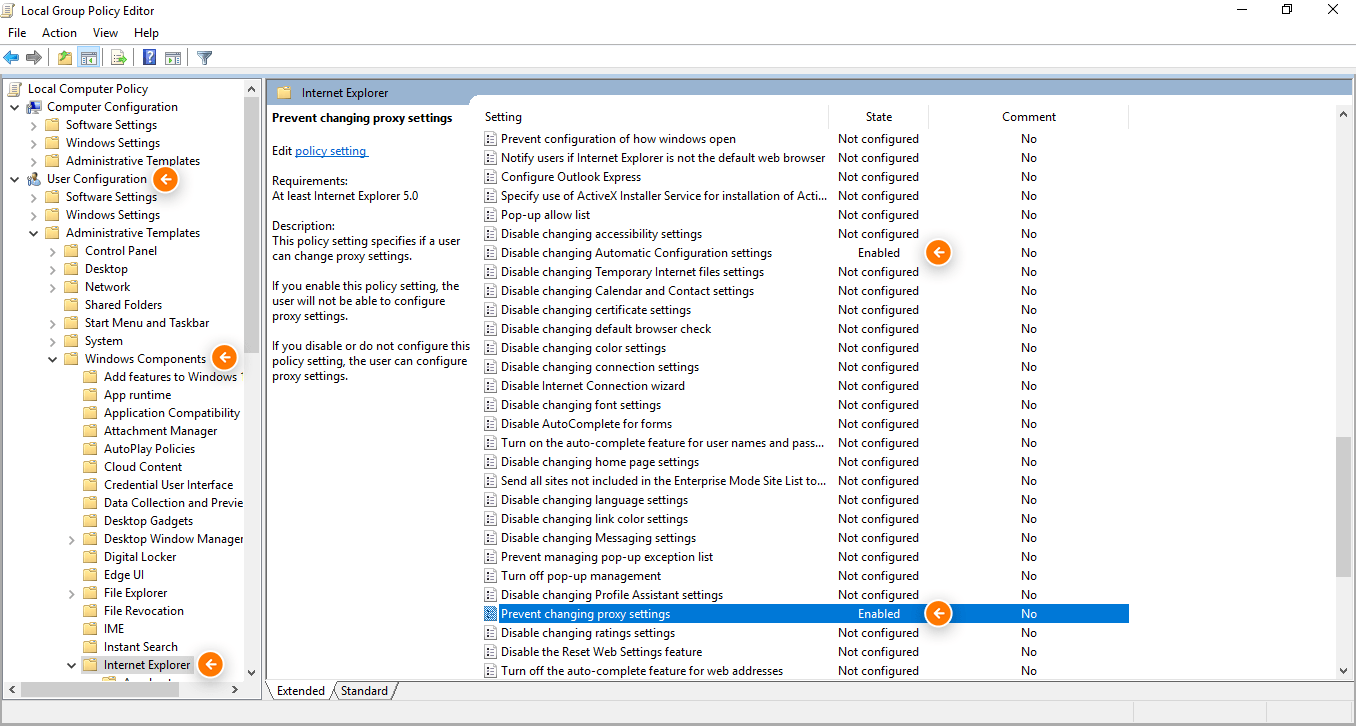
  2. Navigate to User Configuration → Policies → Administrative Templates → Windows Components → Internet Explorer.
  3. Configure the following settings:
    • Disable Changing Automatic Configuration Settings: Set to Enabled.
    • Prevent Changing Proxy Settings: Set to Enabled.
  4. Link this Group Policy Object (GPO) to the organizational unit (OU) containing the users who require these restrictions.Background Image

Step 7: Update and Test the Group Policy

  1. On a computer in the network, run the command gpupdate /force to apply the updated policy.
  2. Log in as a user under the restricted Group Policy and attempt to browse the internet.
  3. Verify that only the websites listed in the Exceptions section are accessible, while all others are blocked.

Result

After completing these steps, all users under the configured Group Policy will only have access to the specific websites listed. Access to all other websites will be blocked by the proxy server settings.

If further adjustments are required, revisit the Group Policy settings or modify the LAN proxy exceptions.

Apply Restrictions to All Users via Group Policy

Once you’ve configured the necessary LAN settings to block all websites except for specific ones, you can enforce these settings across multiple users by using Group Policy.

This step ensures that all users in a designated group or organizational unit (OU) are restricted from accessing unauthorized websites.

Step 1: Open the Group Policy Management Console (GPMC)

  1. On your Windows Server, press Win + R to open the Run dialog box.
  2. Type gpmc.msc and press Enter.
    • This will open the Group Policy Management Console.
    • Ensure you have administrative privileges to access and modify Group Policy Objects (GPOs).

Step 2: Create a New Group Policy Object

  1. In the GPMC, expand the Forest and Domains trees to locate your domain.
  2. Right-click the desired Organizational Unit (OU) that contains the users you want to restrict.
  3. Select Create a GPO in this domain, and Link it here.
  4. Name the new GPO something descriptive, like “Restrict Web Access.”

Step 3: Configure Group Policy Settings for Proxy Restrictions

  1. Right-click the new GPO and select Edit.
  2. In the Group Policy Management Editor, navigate to the following path:
    User Configuration → Policies → Administrative Templates → Windows Components → Internet Explorer.
  3. Configure the following settings:
    • Disable Changing Automatic Configuration Settings:
      • Double-click this policy.
      • Set it to Enabled.
      • Click Apply, then OK.
      • What This Does: Prevents users from modifying the LAN proxy configuration.
    • Prevent Changing Proxy Settings:
      • Double-click this policy.
      • Set it to Enabled.
      • Click Apply, then OK.
      • What This Does: Ensures users cannot bypass the restrictions by altering proxy settings.

Step 4: Link the GPO to an Organizational Unit (OU)

  1. Ensure the GPO is linked to the OU containing the user accounts you want to restrict.
  2. If the GPO isn’t already linked:
    • Right-click the OU and select Link an Existing GPO.
    • Select your newly created “Restrict Web Access” GPO from the list and click OK.

Tip: Double-check that the GPO is linked to the correct OU to avoid applying restrictions to unintended users.

Step 5: Apply and Force the Group Policy

  1. Open Command Prompt on the server or any affected workstation.
  2. Run the following command to update and enforce the policy immediately:
    gpupdate /force
  3. Log in as a user within the affected OU to confirm that the Group Policy settings are applied.

Testing the Policy:

  • Attempt to visit a website not listed in the proxy exceptions.
  • Verify that access is denied.
  • Try visiting one of the authorized websites to ensure it loads correctly.

Step 6: Monitor and Troubleshoot (Optional)

  1. If the settings aren’t applying correctly:
    • Check the Group Policy Results tool by running gpresult /R in Command Prompt to verify the applied policies.
    • Ensure the users or devices are within the scope of the GPO.
  2. Confirm DNS and network configurations support the proxy settings to block unauthorized websites.

Result

With these steps, the proxy restrictions are now applied to all users within the specified OU. They will only be able to access the authorized websites listed in the proxy exceptions. This centralized configuration ensures consistent and enforceable browsing rules across your network.

Simplify Website Restrictions & User Management with V2 Cloud

Blocking websites and allowing access only to specific ones is essential for maintaining control over network usage, improving productivity, and protecting against online threats.

Using Group Policy in a Windows Server environment makes this process manageable for administrators, but it can still be time-consuming and complex.

This is where V2 Cloud can simplify things.

With V2 Cloud’s fully managed Desktop-as-a-Service (DaaS) solution, you can quickly create secure, controlled virtual environments where internet access policies are easy to set up and enforce.

The platform enables centralized management, so you can define access rules for all users with just a few clicks, with no need for complicated server configurations or Active Directory.

Key Benefits of Using V2 Cloud:

  • Effortlessly manage user permissions and website restrictions in one centralized platform.
  • Ensure security and compliance with built-in monitoring and threat protection.
  • Save time with an intuitive interface designed for IT teams and business owners alike.

Talk to a Cloud Expert Now and experience a smarter way to secure and manage your virtual desktops today!

You might also like...

Back to top

Still have questions?

Let us help you find the solution that fits your business.

Schedule a call
Your V2 CloudCare team — real people, on the line.
On a call now34s avg. pickup
SL FC AR MK +6

Your V2 CloudCare team — real people, on the line.