How to Configure GPO Scripts for Login and Startup Tasks on Windows Server®
July 25, 2026

July 25, 2026
Group Policy Objects (GPOs) are a powerful feature in Windows Server that lets administrators automate repetitive tasks and enforce policies across multiple systems. One of the most common uses is a GPO logon script, which runs automatically whenever a user signs in to their account.These GPO scripts can help configure user environments, run security checks, or manage network resources, saving time and ensuring consistency.
This guide walks you through configuring GPO scripts in Windows Server, including creating, assigning, and applying them effectively.
gpupdate /force and test before deploying broadly.Understanding GPO Scripts
Step-by-Step Guide to Configuring GPO Scripts
Simplify GPO Script Management with V2 Cloud
A GPO logon script saves you from configuring each machine by hand. You write the script once, attach it to a Group Policy Object, and link that policy to the right organizational unit (OU).
The next time users sign in, the script runs on its own: mapping network drives, connecting printers, or setting environment variables. Set up correctly, a single GPO logon script keeps every user in that OU on an identical configuration, which cuts down on the repeat support tickets that eat your Monday mornings.
That puts the exact phrase in the opening (once) and the new paragraph (twice), so three natural uses up top without touching the rest of the post.
Group Policy Objects (GPOs) are tools that administrators use to manage settings and automate tasks across multiple systems in a Windows Server environment.
Among their many features, GPOs allow for running scripts during specific events, such as:
Scripts used with GPOs typically come in various formats, including:
The choice of script type depends on the task and the tools available in your environment. Administrators often prefer PowerShell scripts for their flexibility and modern capabilities.
A key benefit of GPO scripts is their ability to enforce consistency. By applying scripts through GPOs, you ensure that users and systems receive the same configurations, reducing errors and manual interventions.
However, it’s crucial to test these scripts in a controlled environment to prevent issues on production systems.
Configuring scripts with Group Policy Objects (GPOs) in Windows Server involves several key steps. These steps allow administrators to set up automated tasks that execute during user logon/logoff or computer startup/shutdown.
New-PSDrive -Name Z -PSProvider FileSystem -Root "\\ServerName\SharedFolder" -Persist


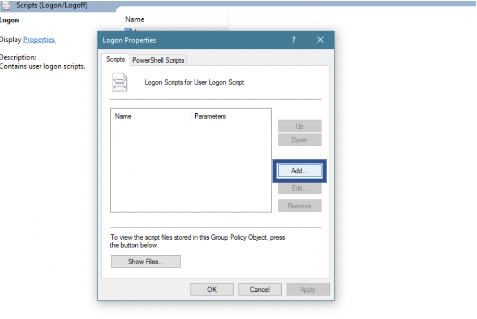

gpupdate /forceGroup Policy Objects give administrators a reliable way to automate sign-in configurations and system startup tasks across a Windows domain. Set them up once and they run on their own.
Follow the steps in this guide and you can create, configure, and deploy scripts that keep your Windows Server environment consistent while cutting down on the manual errors that creep in when every machine is handled by hand.
The trouble starts at scale. Managing scripts and policies across dozens of machines gets messy fast, especially when your users are remote or spread across offices.
That’s where V2 Cloud fits in. We run a fully managed Desktop as a Service (DaaS) platform that hosts your Windows desktops in the cloud, so your GPOs, including every GPO logon script, apply to environments we keep centralized and monitored for you.
Here’s what that looks like in practice:
Pairing GPOs with hosted Windows cloud desktops means faster provisioning and one less fleet of physical machines to patch. Your policies still do the work. We just handle the infrastructure underneath them.
Want to see how this works with your own logon scripts? Talk to a cloud expert.
GPO scripts are scripts that run automatically through Group Policy Objects during events like user logon, logoff, startup, or shutdown. Administrators use them to enforce consistent configurations across many machines at once, which reduces manual setup and cuts down on errors. Set them up once and they apply to every user or computer in the targeted organizational unit.
Logon and logoff scripts attach to user accounts and run when a user signs in or out, making them ideal for user-level tasks like mapping drives or configuring printers. Startup and shutdown scripts attach to computer accounts and run when the machine boots or powers down, which suits system-level tasks like applying updates or clearing temporary files.
You can use PowerShell (.ps1), batch files (.bat), or legacy VBScript (.vbs). PowerShell is the preferred choice for modern environments because it handles complex logic and integrates with Windows Management Instrumentation. Batch files still work fine for simple command-line tasks, and VBScript is mainly for older systems.
Open Command Prompt as an administrator on the target machine and run gpupdate /force. This refreshes the policy without waiting for the default refresh interval. Then sign out and back in, or restart the machine, to confirm the script runs as intended.
The most common causes are a policy that hasn’t refreshed yet, a script stored in a folder the account can’t read, or a GPO linked to the wrong organizational unit (OU). Run gpupdate /force, confirm the folder permissions allow read and execute, and check that the OU actually contains the affected users or computers.
Yes. Always test scripts in a controlled environment before rolling them out to production. A script that runs fine on your machine can behave differently at scale, and a broken logon or startup script can affect every user in the OU at once.

Your V2 CloudCare team — real people, on the line.


