An IPsec VPN (Internet Protocol Security Virtual Private Network) is a powerful tool for securing data transmission across public networks. It encrypts and authenticates each data packet, creating a secure tunnel for communication. This makes it ideal for businesses needing safe and reliable connectivity between remote office locations.
A site-to-site VPN connects entire networks, enabling seamless communication as if all devices were on the same local network. This is especially useful for organizations with multiple offices that need to share resources securely and efficiently.
However, setting up a site-to-site IPsec VPN can be challenging. Configuration errors—such as mismatched encryption settings, weak pre-shared keys, or improper firewall rules—can expose sensitive information or prevent the tunnel from functioning.
This guide simplifies the process, offering a step-by-step walkthrough to help you configure an IPsec VPN for site-to-site communication, ensuring your data remains secure. Let’s get started!
IN THIS GUIDE
What is a Site-to-Site IPsec VPN?
Step 1: Preparing for IPsec Configuration
Step 2: Configuring Site A: Lagos Office
Step 3: Configuring Site B: New York Office
Step 4: Verifying the IPsec VPN Tunnel
Common IPsec Configuration Mistakes and How to Avoid Them
Recommended Method: Simplify VPN Management with V2 Cloud
WordPress Table of Contents by Topic
What is a Site-to-Site IPsec VPN?
A site-to-site IPsec VPN is a secure virtual connection that links two separate networks, such as office locations, using the IPsec protocol. It ensures encrypted data transmission over the Internet or other public networks, creating a private communication channel.
Key Features:
- No Client Software Required: Devices on each network communicate directly without additional software installations.
- Data Encryption: Protects information by encoding it during transit, preventing unauthorized access.
- Secure Tunnel: Establishes a virtual pathway that behaves like a direct router connection between the networks.
IPsec VPN Use Case
Imagine connecting a company’s offices in Lagos and New York. By configuring a site-to-site IPsec VPN, these locations can share files and applications securely as if they were part of the same local network.
This setup is especially valuable for businesses with distributed teams that rely on real-time collaboration and resource sharing. With its robust security and reliability, a site-to-site IPsec VPN is a cornerstone of modern business communication.
Step 1: Preparing for IPsec Configuration
Setting up a site-to-site IPsec VPN requires careful preparation to ensure compatibility and security. Both sites must have consistent settings, and the network infrastructure must support IPsec.
Follow these steps to prepare for a seamless configuration:
1. Ensure Network Compatibility
- Confirm that both sites use routers or firewalls that support IPsec. Most enterprise-grade devices from brands like Cisco, Fortinet, and MikroTik have built-in IPsec support.
- Verify that both networks have unique LAN subnets to prevent IP conflicts. For example:
- Site A (Lagos Office): LAN Subnet: 10.3.0.0/24
- Site B (New York Office): LAN Subnet: 10.5.0.0/24
2. Define Site Information
Before starting, collect and document network details for each site. These details will be used to configure the IPsec profiles and establish the tunnel.
Below is an example setup:
| Site |
Site A (Lagos Office) |
Site B (New York Office) |
|
WAN IP
|
196.52.100.3
|
201.0.115.2 |
| LAN Subnet |
10.3.0.0/24 |
10.5.0.0/24
|
| LAN Gateway IP |
10.3.0.1 |
10.5.0.1 |
3. Choose Authentication and Encryption Settings
Both sites must use identical security settings. Below are the recommended configurations:
- Authentication Method: Pre-shared key (PSK).
- Select a strong key that combines uppercase, lowercase, numbers, and special characters (e.g., My$tr0ngK3y!2024).
- Share the key securely with the other site. Avoid using email unless encrypted.
- Encryption Algorithm: AES-256 (Advanced Encryption Standard). This provides robust encryption to secure transmitted data.
- Hash Algorithm: Use SHA-256 or a stronger option supported by both sites.
- DH Group (Diffie-Hellman): Set to modp2048 for balanced security and performance. If you need enhanced security, consider higher groups like modp4096 but note that it may require a stronger CPU.
4. Plan Tunnel Policies
Plan how traffic will flow through the VPN tunnel:
- Allowed Traffic: Decide whether to allow all traffic or restrict specific types (e.g., HTTP, FTP, or specific ports).
- Firewall Rules: Ensure firewall settings permit traffic to and from the tunnel. By default, most firewalls block VPN traffic, so rules must be configured on both sites.
5. Verify Internet Access
Both sites must have stable internet connections with public-facing WAN IP addresses. Dynamic IP addresses are not recommended, as they can disrupt the tunnel.
If dynamic IPs are unavoidable, consider using a Dynamic DNS (DDNS) service.
6. Test Network Connectivity
Perform a connectivity test between the two sites using the public IP addresses. Use tools like ping or traceroute to verify there are no issues in reaching the other site.
7. Pre-Configuration Checklist
Before proceeding, ensure the following:
- Both sites have compatible routers/firewalls.
- WAN and LAN IPs are properly assigned and documented.
- Encryption and authentication settings are consistent across both sites.
- Firewall rules are adjusted to allow VPN traffic.
- Pre-shared keys are securely shared and stored.
By completing these steps, you’re ready to move on to configuring the IPsec VPN tunnel, ensuring a smooth and secure connection between your networks.
Step 2: Configuring Site A: Lagos Office
Setting up Site A for the site-to-site IPsec VPN involves three main steps: Phase 1 configuration, Phase 2 configuration, and firewall rule adjustments.
These settings define how Site A communicates with Site B and ensure the tunnel’s security and reliability. Below is a detailed guide for configuring Site A.
1. Phase 1 Configuration (IKE Phase 1)
Phase 1 is responsible for authenticating and negotiating the secure connection between Site A and Site B. It establishes the foundation of the VPN tunnel by exchanging keying material and authentication information.
- Access the Router’s IPsec Section:
- Log in to the router’s management interface.
- Navigate to the IPsec or VPN Settings section, depending on your router model.
- Create a New Phase 1 Profile:
- Click Add Profile or New Connection to start creating a profile.
- Configure Phase 1 Settings: Fill in the settings as follows:
- Name: Give the profile a descriptive name, such as IPsec_SiteA.
- Authentication Method: Select Pre-Shared Key (PSK).
- My Identifier: Use the router’s default identifier (e.g., WAN IP or hostname).
- Peer Identifier: Use the WAN IP or hostname of Site B (201.0.115.2 in this example).
- Pre-Shared Key: Input a strong, secure key (e.g., My$trongKey123!) and securely share it with Site B.

- Set Encryption and Authentication Parameters:
- Encryption Algorithm: Choose AES-256 for strong encryption.
- Hash Algorithm: Use SHA-256 (or the strongest hash supported by both sites).
- Diffie-Hellman (DH) Group: Select modp2048 or higher for key exchange.

- Lifetime and Advanced Options:
- Lifetime: Set to a reasonable duration, such as 28800 seconds (8 hours).
- IKE Version: Use IKEv2, as it is faster and more secure than IKEv1, if supported.
- Leave other settings as default unless specific requirements dictate otherwise.
- Save and Apply:
- Once all settings are configured, save the profile.
2. Phase 2 Configuration (IKE Phase 2)
Phase 2 builds on the Phase 1 tunnel to establish the data path, allowing secure communication between the local and remote subnets.
- Create a New Phase 2 Profile:
- In the IPsec or VPN section, locate Phase 2 Settings or Child SA.
- Click Add Profile or New Connection.
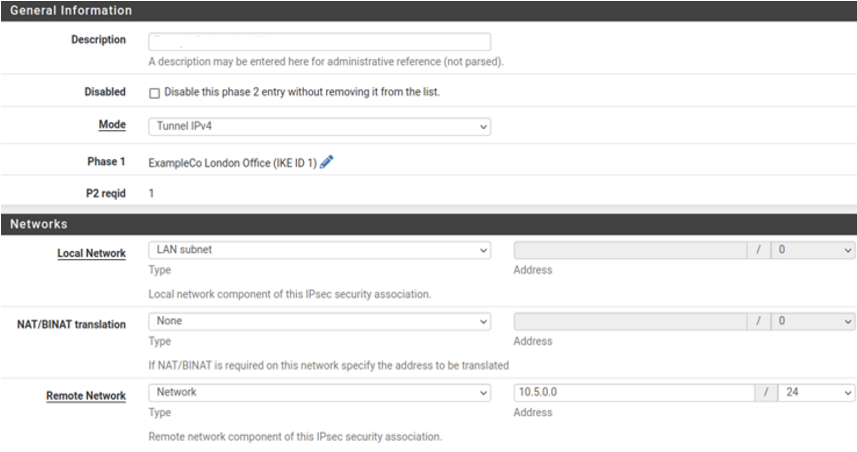
- Configure Phase 2 Settings: Input the following details:
- Description: Name the Phase 2 profile (e.g., IPsec_Phase2_SiteA).
- Mode: Select Tunnel IPv4.
- Local Network: Set this to Site A’s LAN Subnet (10.3.0.0/24).
- Remote Network: Set this to Site B’s LAN Subnet (10.5.0.0/24).
- NAT/BINAT: Choose None unless NAT is required for your specific setup.
- Encryption and Authentication Parameters:
- Protocol: Select ESP (Encapsulating Security Payload).
- Encryption Algorithm: Use AES-GCM if supported, as it combines encryption and authentication for better performance.
- Hash Algorithm: Leave blank if using AES-GCM; otherwise, select the strongest hash supported by both sites (e.g., SHA-256).

- Lifetime and Advanced Options:
- Lifetime: Set to a value slightly lower than Phase 1 (e.g., 27000 seconds or 7.5 hours).
- Leave other settings as default unless specific adjustments are required.
- Save and Apply:
- Save the profile and apply the settings to activate Phase 2.
3. Firewall Configuration
By default, most routers block traffic from remote VPN hosts. To allow communication between Site A and Site B, adjust the firewall settings on Site A’s router.
- Access Firewall Settings:
- Navigate to the router’s Firewall or Security section.
- Create IPsec-Specific Rules:
- In the IPsec tab, add a rule to allow traffic through the VPN tunnel.
Example rule:
- Source: Site B’s LAN Subnet (10.5.0.0/24).
- Destination: Site A’s LAN Subnet (10.3.0.0/24).
- Protocol: Allow all protocols or specify specific ones (e.g., TCP, UDP, ICMP).
- Save and Apply Rules:
- Save the firewall configuration and ensure the rule is enabled.
4. Final Steps for Site A
- Verify Settings:
- Double-check that all IPsec profiles and firewall rules are consistent with Site B’s expected configuration.
- Generate Traffic:
- Ping an IP in Site B’s LAN subnet from a device in Site A’s LAN subnet to test the tunnel.
Once Site A is fully configured, proceed to configure Site B with corresponding settings.
Step 3: Configuring Site B: New York Office
The process of configuring Site B (New York Office) is similar to configuring Site A, but with adjustments to reflect Site B’s network details and its role as the second endpoint in the VPN connection.
This section provides detailed steps for Phase 1 configuration, Phase 2 configuration, and firewall rule adjustments to complete the site-to-site IPsec VPN setup.
1. Phase 1 Configuration (IKE Phase 1)
Phase 1 establishes the secure tunnel and handles the initial exchange of keys and authentication between the two sites.
- Access the Router’s IPsec Section:
- Log in to the management interface of Site B’s router.
- Navigate to the IPsec or VPN Settings section.
- Create a New Phase 1 Profile:
- Click Add Profile or New Connection to begin.
- Configure Phase 1 Settings: Fill in the following details to match Site A’s Phase 1 configuration:
- Name: Name the profile, such as IPsec_SiteB.
- Authentication Method: Select Pre-Shared Key (PSK).
- My Identifier: Use the router’s default identifier (e.g., WAN IP or hostname).
- Peer Identifier: Input the WAN IP of Site A (196.52.100.3).
- Pre-Shared Key: Use the same strong key shared with Site A (e.g., My$trongKey123!).
- Set Encryption and Authentication Parameters:
- Encryption Algorithm: Select AES-256.
- Hash Algorithm: Use SHA-256 or a supported strong hash algorithm.
- Diffie-Hellman (DH) Group: Set to modp2048 or higher.
- Lifetime and Advanced Options:
- Lifetime: Set slightly higher than Site A’s value, e.g., 32000 seconds (8.9 hours).
- IKE Version: Use IKEv2 if supported for better performance and security.
- Save and Apply:
- Save the profile to finalize the Phase 1 configuration.
2. Phase 2 Configuration (IKE Phase 2)
Phase 2 specifies the data flow parameters for the secure tunnel and establishes encryption for communication between LAN subnets.
- Create a New Phase 2 Profile:
- In the IPsec or VPN section, locate Phase 2 Settings or Child SA.
- Click Add Profile or New Connection.
- Configure Phase 2 Settings: Match these settings to Site A, with adjustments for Site B’s network:
- Description: Name the Phase 2 profile, such as IPsec_Phase2_SiteB.
- Mode: Select Tunnel IPv4.
- Local Network: Enter Site B’s LAN Subnet (10.5.0.0/24).
- Remote Network: Enter Site A’s LAN Subnet (10.3.0.0/24).
- NAT/BINAT: Choose None, unless NAT is required for specific use cases.
- Encryption and Authentication Parameters:
- Protocol: Select ESP (Encapsulating Security Payload).
- Encryption Algorithm: Use AES-GCM if available, or AES-256 if not.
- Hash Algorithm: If using AES-GCM, leave the hash field blank. Otherwise, use the strongest supported hash (e.g., SHA-256).
- Lifetime and Advanced Options:
- Lifetime: Set slightly higher than Site A’s Phase 2 (e.g., 30000 seconds or 8.3 hours).
- Save and Apply:
- Save the profile to activate Phase 2 settings.
3. Firewall Configuration
Firewall rules must allow traffic from Site A through the VPN tunnel. By default, most firewalls block traffic from remote VPN hosts.
- Access Firewall Settings:
- Go to the router’s Firewall or Security section.
- Add IPsec Firewall Rules:
- Create a rule to permit traffic through the tunnel. Use the following parameters:
- Source: Site A’s LAN Subnet (10.3.0.0/24).
- Destination: Site B’s LAN Subnet (10.5.0.0/24).
- Protocol: Allow all protocols, or restrict to specific protocols (e.g., TCP, UDP, ICMP).
- Save and Apply Rules:
- Save the changes and ensure the rule is enabled.
4. Final Steps for Site B
- Verify Consistency with Site A:
- Double-check that all Phase 1 and Phase 2 settings match Site A’s configuration, with the appropriate adjustments for Site B’s network.
- Test Connectivity:
- Generate traffic from Site B to Site A (e.g., ping a device in Site A’s LAN subnet) to verify the tunnel is functioning.
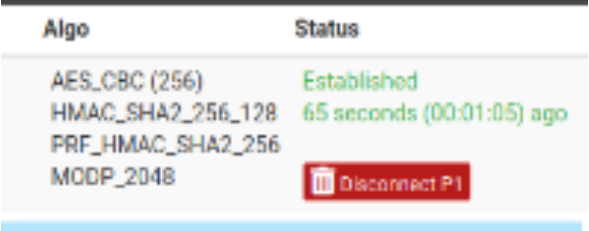
- Check VPN Status:
- Navigate to Status > IPsec or a similar section in the router interface. Ensure the tunnel is listed as “Established."
If the tunnel does not appear as established, review the settings for mismatches in pre-shared keys, encryption parameters, or firewall rules. Additionally, ensure traffic has been generated to initiate the tunnel.
Once Site B’s configuration is complete, the site-to-site IPsec VPN should be fully operational, providing secure communication between the two networks.
Step 4: Verifying the IPsec VPN Tunnel
After configuring both sites, it’s essential to verify that the site-to-site IPsec VPN is active and functioning as intended. This step ensures the tunnel is established and allows secure communication between the two networks.
1. Check VPN Status
Most routers and firewalls provide a status page for VPN connections. Follow these steps to confirm the tunnel’s status:
- Access the Router’s Management Interface:
- Log in to the router for each site.
- Navigate to the IPsec Status Section:
- Go to Status > IPsec or a similar tab (varies by device).
- Verify Tunnel Status:
- Look for the tunnel profile name (e.g., IPsec_SiteA_to_SiteB).
- The status should show as “Established" or “Active" for both sites.
- Check details like uptime, data exchanged, and the active phase (both Phase 1 and Phase 2 should be operational).
2. Test Connectivity Between Sites
To ensure the tunnel is passing traffic, perform a connectivity test from one site to the other.
- Ping a Device on the Remote Network:
- From a device on Site A’s LAN, ping the IP address of a device on Site B’s LAN, and vice versa.
- Example: From a computer with IP 10.3.0.2 at Site A, ping the IP 10.5.0.2 at Site B.
- Successful Test Indicators:
- Replies to the ping requests indicate that the tunnel is working.
- If pings fail, check the firewall rules and ensure IPsec is set to allow traffic between LAN subnets.
3. Generate Tunnel Traffic
IPsec tunnels may not be established until traffic is sent between the sites. If the tunnel status shows “Inactive" or “Disconnected," force the tunnel to activate by:
- Sending Traffic:
- Transfer a file, access a shared network folder, or perform a traceroute between the sites.
- Rechecking Status:
- Return to the IPsec status page and confirm that the tunnel is now established.
4. Troubleshoot Common Issues
If the tunnel does not establish or traffic is not passing through, consider the following troubleshooting steps:
- Pre-Shared Key Mismatch:
- Ensure the same pre-shared key is configured on both Site A and Site B.
- Encryption/Authentication Settings:
- Verify that both sites use identical encryption, hash, and DH group settings.
- Firewall Rules:
- Check that IPsec traffic is allowed on both routers, including LAN-to-LAN traffic.
- IP Address Conflicts:
- Confirm that both sites use unique LAN subnets to avoid routing issues.
- Lifetime Settings:
- Ensure Phase 1 and Phase 2 lifetimes are properly aligned between the sites.
5. Monitoring and Logging
Enable logging on your routers or firewalls to identify potential issues with the IPsec VPN:
- Enable Debugging Logs:
- Turn on IPsec-related logs to see details about Phase 1 and Phase 2 negotiations.
- Look for Errors:
- Common errors include “No Proposal Chosen" (encryption mismatch) or “Authentication Failed" (pre-shared key issues).
- Adjust and Retest:
- Resolve errors based on the logs and recheck the status.
6. Confirm Secure Data Transmission
Finally, verify that data transmitted between the sites is secure:
- Capture Traffic:
- Use a network monitoring tool (e.g., Wireshark) to ensure data is encrypted when traveling between Site A and Site B.
- Confirm Encryption:
- Look for encrypted packets, confirming that the IPsec tunnel is securing the data.
Common IPsec Configuration Mistakes and How to Avoid Them
Setting up a site-to-site IPsec VPN can be challenging, especially if configuration errors occur. These mistakes can lead to failed connections or security vulnerabilities.
Below are some of the most common issues encountered during setup and how to resolve them.
| Mistake |
Problem |
Solution |
| Mismatched Pre-Shared Keys |
The VPN tunnel fails to establish if keys don’t match between sites. |
Double-check and securely share the same pre-shared key for both sites. Use a strong key like My$ecureK3y!. |
| Inconsistent Encryption/Hash Settings |
Mismatched algorithms prevent secure negotiation of the tunnel. |
Ensure both sites use identical settings: AES-256 for encryption, SHA-256 for hash, and modp2048 for DH Group. |
| Overlapping LAN Subnets |
Routing conflicts occur if both sites use the same LAN subnet. |
Assign unique LAN subnets to each site (e.g., 10.3.0.0/24 for Site A, 10.5.0.0/24 for Site B) or use NAT to avoid conflicts. |
| Incorrect Firewall Rules |
Traffic is blocked, preventing communication through the tunnel. |
Add rules allowing IPsec traffic between LAN subnets. For example: Source: 10.5.0.0/24, Destination: 10.3.0.0/24, Protocol: All or specific (e.g., TCP, UDP, ICMP). |
| Mismatched Lifetimes |
The tunnel disconnects prematurely or fails to establish. |
Align lifetimes across both sites (e.g., 28800 seconds for Phase 1 and 27000 for Phase 2). Site B can use slightly higher lifetimes for smoother re-negotiation. |
| Not Generating Traffic |
The tunnel doesn’t activate until traffic crosses the connection. |
Ping a device on the remote network or access shared resources to initiate traffic and activate the tunnel. |
| Dynamic IP Addresses Without DDNS |
VPN breaks when dynamic WAN IP changes. |
Use a Dynamic DNS (DDNS) service to assign a hostname to the dynamic IP and configure remote gateways to use the hostname instead of a static IP. |
| Ignoring Logs and Debugging Tools |
Issues become hard to diagnose without logging errors. |
Enable IPsec logs on both routers. Look for errors like “Authentication Failed" (key mismatch) or “No Proposal Chosen" (encryption mismatch), and adjust settings based on log messages. |
| Overloading Router CPU |
High encryption settings or DH Group values slow down or crash the router. |
Use balanced settings like AES-256 and modp2048. Upgrade to a higher-performance router if necessary. |
| Neglecting Backup Configurations |
Configuration changes or mistakes disrupt the VPN. |
Export and save backup configurations after setup. Store backups securely for both sites to quickly restore settings if issues arise. |
Recommended Method: Simplify VPN Management with V2 Cloud
Configuring a site-to-site IPsec VPN can be time-consuming and technically complex.
From ensuring consistent encryption settings to troubleshooting mismatched configurations, the process demands expertise and attention to detail. Even after setup, maintaining and monitoring the VPN can be an ongoing challenge.
V2 Cloud eliminates the complexities of managing VPNs by providing secure, reliable, and hassle-free cloud infrastructure. Here’s how we make your life easier:
- Simplified Deployment: No need for intricate router configurations or advanced networking knowledge. V2 Cloud virtual desktops and servers are pre-configured to connect securely over the internet.
- Enterprise-Grade Security: Our cloud infrastructure includes built-in protections like data encryption and secure access, ensuring your information remains safe without needing to manage IPsec or other VPN protocols.
- Scalable Solutions: Easily expand your network by adding virtual desktops or servers as your business grows—no need to configure additional tunnels or network rules.
- Centralized Management: Manage all your resources in one place through a user-friendly dashboard. Monitor activity, adjust settings, and control access with just a few clicks.
- Save Time and Resources: With V2 Cloud, you can focus on your core business tasks while we handle the technical details. Avoid spending hours troubleshooting VPN issues or worrying about configuration errors.
Whether you’re connecting remote teams, sharing sensitive data, or managing distributed resources, our platform offers a seamless, secure alternative to traditional VPN setups.
Talk to a Cloud Expert Today and experience secure, stress-free connectivity!




