How to Disable Copy and Paste in Windows®: For Local Machines and VMs
March 18, 2025

March 18, 2025
Copy and paste functionality can be a major security risk.
It allows unauthorized data transfer between a local machine and a Virtual Machine (VM), potentially exposing sensitive information or violating security protocols. This is especially critical in environments where compliance with strict data protection policies is required.
The solution? Disable copy and paste for all users.
Whether you’re managing a team or ensuring your VM stays secure, this guide will walk you through step-by-step instructions for disabling clipboard redirection. You’ll learn how to block copy and paste for all users, including administrators, using the Windows Group Policy Editor.
Why Disable Copy and Paste in Windows?
How to Disable Copy and Paste for All Users: Step-by-Step Tutorial
Step 1: Open the Group Policy Editor
Step 2: Navigate to the Clipboard Redirection Setting
Step 3: Disable Clipboard Redirection
Step 4: Verify the Changes
Additional Tips for Managing Clipboard Redirection
Secure Your Remote Desktop Environment with V2 Cloud
Disabling copy and paste in Windows is essential for protecting sensitive data and maintaining system security. Clipboard redirection, which allows users to transfer data between a local machine and a VM, may seem convenient but can lead to several risks.
Here’s why you should disable it:
Allowing clipboard redirection opens the door to potential data breaches. Users can easily copy sensitive information from the VM to their local device or introduce malicious content into the VM. By disabling this feature, you can block this vulnerability and reduce the risk of unauthorized data sharing.
Organizations that deal with confidential or regulated information, such as financial institutions or healthcare providers, must adhere to strict data security standards. Disabling copy/paste helps ensure compliance with frameworks like GDPR, HIPAA, or ISO 27001 by preventing unauthorized data transfer.
The clipboard can act as a pathway for malware or unwanted scripts. For example, malicious content copied on a local device could easily be pasted into the VM, compromising its security. Disabling clipboard redirection eliminates this risk, protecting both the local machine and the VM.
By disabling copy and paste, administrators can enforce stricter controls on the system. This prevents end-users from bypassing organizational policies and ensures a consistent security posture across all devices.
To disable copy and paste between a local machine and a Virtual Machine (VM), you’ll need to adjust settings in the Windows Group Policy Editor. This process ensures all users, including administrators, cannot transfer data through clipboard redirection.
The Group Policy Editor allows you to manage advanced Windows settings. Follow these steps to access it:
This will open the Group Policy Management Console, where you can modify system policies.
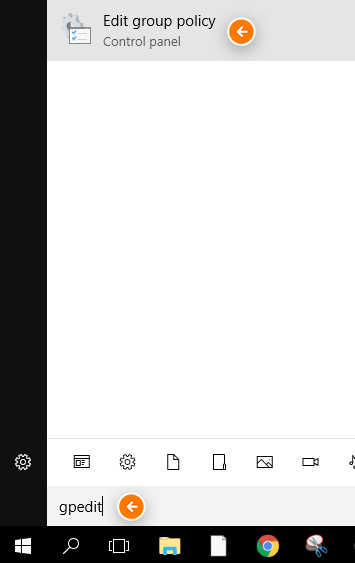
Once the Group Policy Editor is open, you’ll need to locate the setting that controls clipboard redirection.
You are now in the section where clipboard redirection settings can be configured.

With the correct section open, follow these steps to disable the clipboard redirection feature:
You have now successfully disabled the ability for users to copy and paste between their local device and the VM.

To ensure the setting is applied correctly:
Disabling clipboard redirection is an effective security measure, but to ensure it’s implemented properly and aligns with your broader security goals, consider these additional tips:
Making changes to Group Policy settings requires administrator rights. Before starting, confirm that you are logged in as an administrator on the local machine. Without the correct permissions, you may not be able to access or modify the necessary settings.
Clipboard redirection is just one aspect of Remote Desktop security. For a more robust setup, explore additional settings in the Group Policy Editor, such as:
Implementing these settings can further secure your remote desktop environment.
After enabling the policy to block clipboard redirection, verify that the changes are effective:
Testing ensures that no gaps remain in your security setup.
For larger environments, consider applying these settings using Group Policy Objects (GPOs) in Active Directory. This method allows you to enforce clipboard redirection restrictions across multiple machines or users at once, ensuring consistency.
Even with clipboard redirection disabled, users may still find other ways to transfer data. Provide training or guidelines on secure practices, such as:
Educating users helps align their behavior with your security goals.
Disabling copy and paste is a crucial step in securing your remote desktop environment. It prevents unauthorized data sharing, protects against malware, and ensures compliance with security policies.
By following the steps outlined in this guide, you’ve taken an important step toward safeguarding your Virtual Machine.
But why stop there? With V2 Cloud, you can enjoy secure, high-performance cloud desktops designed with your business needs in mind.
Our platform offers built-in security features, including restricted clipboard access, centralized control, and seamless user management, all without the hassle of manual configurations.
Take control of your virtual desktop security with V2 Cloud. Experience easy setup, enhanced security, and a support team that’s here to help every step of the way.
Talk to a Cloud Expert Today! Explore how we will simplify and secure your remote desktop experience.

Your V2 CloudCare team — real people, on the line.


