Shared folders only help your team if people can reach them easily. For one computer, mapping a drive takes a few clicks. For a whole company, doing it by hand quickly becomes a support headache. This guide shows how to map a network drive three ways:
- Manually in File Explorer
- From the command line
- Centrally with Group Policy drive mapping
The Group Policy method is the one to use when you need to map a drive for all users in your organization. By the end, you’ll know how to:
- Map a drive on a single Windows PC
- Create and link a Group Policy Object (GPO)
- Configure drive maps with item-level targeting
- Map a drive for all users in your domain
- Troubleshoot drives that don’t appear
How to Map a Network Drive in File Explorer
If you only need a mapped drive on one computer, File Explorer is the quickest option.
- Open File Explorer and select This PC.
- Click the three-dot menu (Windows 11) or the Computer tab (Windows 10), then choose Map network drive.
- Pick a drive letter from the dropdown.
- In Folder, enter the network path, for example \\ServerName\ShareName, or click Browse.
- Check Reconnect at sign-in so the drive comes back after a restart.
- If the share needs different credentials, check Connect using different credentials.
- Click Finish.
This works well for a single user. It doesn’t scale, though: every PC has to be set up separately, and you can’t enforce consistency.
How to Map a Network Drive with Command Prompt
For quick fixes or scripting, use the net use command:
net use S: \\ServerName\ShareName /persistent:yes
To remove a mapped drive:
net use S: /delete
PowerShell users can use New-PSDrive -Name “S" -PSProvider FileSystem -Root “\\ServerName\ShareName" -Persist.
Commands are faster than clicking, but they still run per machine or per logon script. For centralized control, Group Policy is the better tool.
What Is Group Policy Drive Mapping?
Group Policy drive mapping is a Group Policy Preferences feature. It lets administrators automatically assign network drives to users in an Active Directory (AD) domain, so users don’t have to set anything up on their devices.
For administrators, Group Policy is the most reliable answer to how to map a network drive across a whole organization. You configure drive assignments once, centrally, and Windows applies them at every logon. Unlike logon scripts, Group Policy drive mapping needs no coding and no script maintenance.
Why Use Group Policy for Drive Mapping?
- Scalability: Map drives for one user, a department OU, or the entire domain.
- Automatic updates: Changes apply at the next logon or policy refresh, with no user action needed.
- Targeting flexibility: Use item-level targeting to assign drives by security group, OU, computer, or other attributes.
- Centralized management: Edit every mapping from the Group Policy Management Console (GPMC).
Prerequisites for Group Policy Drive Mapping
Confirm these are in place before you start.
Administrative access. You need rights to create and link GPOs in the domain, such as Domain Admin or delegated GPO permissions.
A clear OU or group structure. Users should be organized in OUs, such as HR, IT, and Sales, or in security groups. This lets you target the right people.
A shared network folder. The share must:
- Be reachable at a valid UNC path, such as \\ServerName\ShareName
- Have both share permissions and NTFS permissions set for the target users. For example, Read to view files, or Modify to add and edit them.
Test the path from a client machine before continuing.
Domain-joined Windows clients. Windows 10, Windows 11, and current Windows Server versions all support Group Policy Preferences drive maps. The machines must be joined to the domain.
A drive letter plan. Choose letters that won’t clash with local disks or USB drives. For example, H: for HR and S: for Sales.
Step-by-Step: How to Map Network Drives Using GPO
Step 1: Create a New Group Policy Object
- Log in to a domain controller, or a management workstation with RSAT, using an account with GPO permissions.
- Open Server Manager > Tools > Group Policy Management.
- Expand your forest and domain, then right-click Group Policy Objects and select New.
- Give it a descriptive name, such as “Map Accounts Share", and click OK.

Tip: Don’t copy or edit the Default Domain Policy for drive mappings. Keeping drive maps in their own GPO makes them easier to troubleshoot and roll back.
Step 2: Link the GPO to an Organizational Unit
- In GPMC, locate the target OU, such as Sales.
- Right-click the OU and choose Link an Existing GPO, or drag the GPO onto the OU.
- Select your new GPO and click OK.
- Expand the OU and confirm the GPO appears under Linked Group Policy Objects.
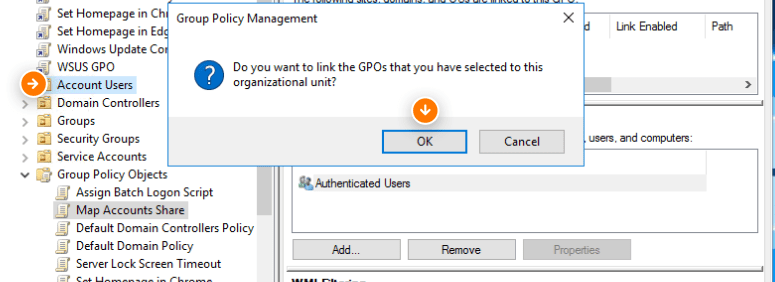
Because drive maps are a user setting, link the GPO to an OU that contains user accounts, not only computer accounts.
Step 3: (Optional): Publish the Shared Folder in Active Directory
Publishing a share in AD makes it easy to find when you browse, but it isn’t required. You can type the UNC path directly in Step 4. To publish the share:
- Open Server Manager > Tools > Active Directory Users and Computers.
- Right-click the target container and select New > Shared Folder.
- Enter a Name, such as “HR Shared Files", and the Network path, such as \\ServerName\ShareName.
- Click OK.
Step 4: Configure the Drive Map
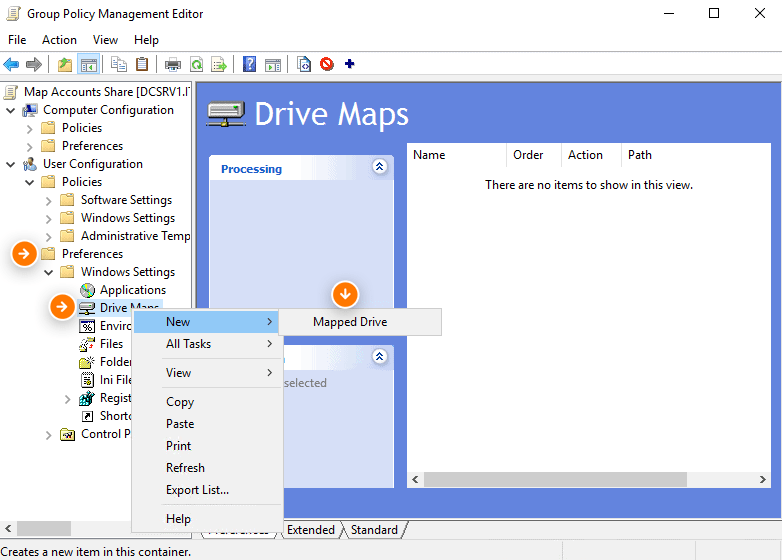
- In GPMC, right-click your GPO and select Edit.
- Go to User Configuration > Preferences > Windows Settings > Drive Maps.
- Right-click Drive Maps and choose New > Mapped Drive.
General tab
- Action: Choose Update. This creates the drive if it’s missing and corrects it if it has changed. It’s the safest default. Use Replace only if you need to force a clean remap every time.
- Location: Enter the UNC path, or click the ellipsis (…) to browse to a published share.
- Reconnect: Check this so the drive persists.
- Label as: Add a friendly name, such as “Sales Files".
- Drive Letter: Choose Use and a specific letter, or Use first available, starting at.


Common tab
-
- Run in logged-on user’s security context: Check this so the drive maps with the user’s own credentials.
- Item-level targeting: Check this if only some users in the OU should get the drive.
Step 5: Set Item-Level Targeting (Optional)
- Click Targeting.
- Select New Item and choose a condition, such as Security Group or Organizational Unit.
- Define the condition, for example members of Sales-Team, and click OK.
Item-level targeting lets a single GPO handle many drive maps, with each one going only to the right group.
Step 6: Apply and Verify
- Click Apply and OK.
- On a client machine, run gpupdate /force from Command Prompt.
- Sign out and back in. Drive maps apply at user logon.
- Open File Explorer > This PC and confirm the drive appears with the correct letter and label.
How to Map a Network Drive for All Users
To map a drive for all users in the domain, rather than one department, adjust how the GPO is scoped:
- Link the GPO at the domain level instead of a single OU. Or link it to every OU that contains user accounts.
- Keep the default security filtering of Authenticated Users, so every domain user receives the policy.
- Skip item-level targeting for the drive map, or target a broad group such as Domain Users.
- Check share and NTFS permissions. Grant Domain Users or Authenticated Users the right level of access. Otherwise the drive will appear but users will get “Access denied."
- Run gpupdate /force on a test machine and confirm with a standard user account.
If some users should not get the drive, such as service accounts or contractors, add an item-level targeting rule with “Is Not" to exclude a specific group.
What about all users on one shared PC?
To map a drive for all users who sign in to a specific computer, use the same user-side drive map. Then enable Loopback Processing (Merge mode) in a GPO linked to that computer’s OU. This lets the user policy apply to anyone who logs on to that machine.
Map Network Drives Troubleshooting Common Issues
-
The GPO isn’t applying
- Confirm the GPO is linked to the OU that contains the user accounts.
- Check that the GPO link is enabled and not blocked by Block Inheritance. Use Enforced only if a higher-level policy genuinely needs to override this.
- Run gpresult /h gpresult.html on the client and look under Applied GPOs. If the GPO is listed under Denied GPOs, check the security filtering.
-
Wrong path or drive letter
- Double-check the Location path in the drive map.
- Make sure the letter isn’t already used by a local disk, USB drive, or another mapping.
- Test the path manually with Win + R and \\ServerName\ShareName.
-
Access denied
- Review both the Sharing tab and the Security (NTFS) tab on the folder.
- Test with a standard account in the target group, not an admin account.
-
Changes don’t show up
- Run gpupdate /force, then sign out and back in.
- Make sure the Group Policy Client service is running.
- Check connectivity to the domain controller with ping DomainControllerName and nltest /dsgetdc:yourdomain.
-
The drive disappears after restart
- Make sure Reconnect is checked and the Action is Update.
- Look for old logon scripts or net use /delete commands that remove the drive.
-
Item-level targeting isn’t working
- Recheck the targeting conditions and any “Is Not" logic.
- Confirm group membership. Users must sign out and back in after being added to a group.
-
Slow logons
- Keep drive maps in one well-organized GPO rather than many small ones.
- Check the file server’s performance and latency.
- Remove mappings to decommissioned servers. Windows waits for unreachable paths.
-
Remote users can’t see the drive
- Drive maps apply at logon, so users connecting over VPN after signing in may not get them until they refresh policy or sign in again.
- Confirm the UNC path is reachable over the VPN.
- Consider Offline Files for critical shares, or move remote users to a cloud desktop so they don’t depend on the office network at all.
How to Map Network Drives FAQ
What is the easiest way to map a drive on one computer?
Use File Explorer > This PC > Map network drive, enter the UNC path, and check Reconnect at sign-in.
Is Group Policy drive mapping better than logon scripts?
In most cases, yes. Group Policy drive mapping has a graphical interface, supports item-level targeting, and needs no script maintenance.
Can I map a drive for all users without Group Policy?
On a single PC you can use a logon script or scheduled task. For a domain, Group Policy is the standard and most reliable method.
Why does my mapped drive show a red X?
Windows can’t reach the share at logon. This usually happens because the network wasn’t ready yet, or the server or VPN is unavailable. Opening the drive often reconnects it.
A Simpler Option for Remote Teams: V2 Cloud
Now you know how to map a network drive manually, from the command line, and with Group Policy. All of these methods share one limitation: they depend on users being connected to your network.
With V2 Cloud, shared files and resources live inside users’ cloud desktops, so there are no GPOs to maintain for remote staff:
- Simplified management: Resources are built into each virtual desktop and managed from one IT management console, with no drive maps or scripts.
- Access from anywhere: Users connect securely from any device, without a VPN, using the web app or the V2 Cloud client.
- Built-in security: Encryption, MFA, and daily backups protect your data.
- Scalable pricing: Add resources as your team grows. See pricing.
Talk to a Cloud Expert to see how V2 Cloud can simplify file access for your team.




