If you’re searching for a secure and efficient way to enable remote access to your network, setting up a Remote Desktop Gateway (RDP Gateway) is the solution.
RD Gateway allows authorized users to connect to internal resources—like servers or remote desktop-enabled PCs—via an encrypted connection using the Remote Desktop Protocol (RDP) over HTTPS.
This setup is ideal for businesses that need to provide remote access without exposing internal server names or IP addresses. With an RD Gateway, you can ensure secure connections from any device while controlling user access through customizable policies.
In this guide, you’ll learn how to configure an RD Gateway in four simple steps—from installing the role to testing the connection. By following these instructions, you’ll create a safe, reliable remote access solution that meets your team’s needs.
IN THIS ARTICLE
What is a Remote Desktop Gateway?
Steps to Set Up a Remote Desktop Gateway
Step 1: Install the Remote Desktop Gateway Role
Step 2: Configure Authorization Policies (CAP & RAP)
Step 3: Install an SSL Certificate
Step 4: Test RD Gateway Connection
Frequently Asked Questions about Remote Desktop Gateway
How V2 Cloud Simplifies Remote Desktop Gateway Setup
WordPress Table of Contents by Topic
What is a Remote Desktop Gateway?
A Remote Desktop Gateway (RD Gateway) is a secure way for remote users to access internal network resources. It uses the Remote Desktop Protocol (RDP) over HTTPS to establish encrypted connections, ensuring that sensitive data remains protected.
RD Gateway allows users to connect to remote desktop session hosts, RemoteApp programs, or computers with remote desktop enabled—regardless of whether these resources have public-facing IPs or domain names.
Why Use a Remote Desktop Gateway?
- Enhanced Security: RD Gateway encrypts connections, making it safe to access internal servers over the internet.
- Flexible Access: Users can connect from any internet-connected device without exposing internal server details.
- Streamlined Resource Management: Administrators can set policies to control who can access which resources, ensuring that permissions are both secure and organized.
Importance of SSL Certificates
For optimal security, an SSL certificate is crucial.
While this tutorial uses a self-signed certificate for demonstration purposes, production environments should use certificates from trusted providers like Comodo, Verisign, or InstantSSL. These certificates enhance trust and ensure compatibility with a wider range of devices and browsers.
Steps to Set Up a Remote Desktop Gateway
Setting up a Remote Desktop Gateway (RD Gateway) involves installing the necessary role, creating authorization policies, adding an SSL certificate, and testing your configuration.
Follow this detailed step-by-step guide to ensure a secure and functional setup.
Step 1: Install the Remote Desktop Gateway Role
- Sign in to the Target Server
- Log in with administrative credentials to the Windows® server where you plan to install the RD Gateway role.

- Open Server Manager
- In the Server Manager dashboard, click Manage, then select Add Roles and Features.

- Select Installation Type
- Choose Role-Based or Feature-Based Installation, and click Next.

- Select Destination Server
- From the Server Pool, select your local server (or the target server for RD Gateway), and click Next.

- Select Server Roles
- Check the box for Remote Desktop Services, and click Next.

- Choose Role Services
- Under Role Services, select Remote Desktop Gateway, then click Next.

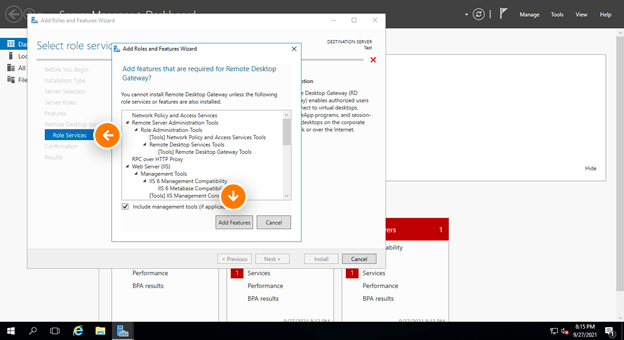
- Add Required Features
- When prompted, click Add Features to install dependencies for RD Gateway.
- Network Policy and Access Services
- On the Network Policy and Access Services page, click Next.

- Web Server Role (IIS)
- Confirm that the Web Server Role (IIS) is selected, and click Next.

- Role Services for IIS
- Leave the default role services selected for IIS, and click Next.

- Confirm Installation Selections
- Review the selected roles and features, then click Install.
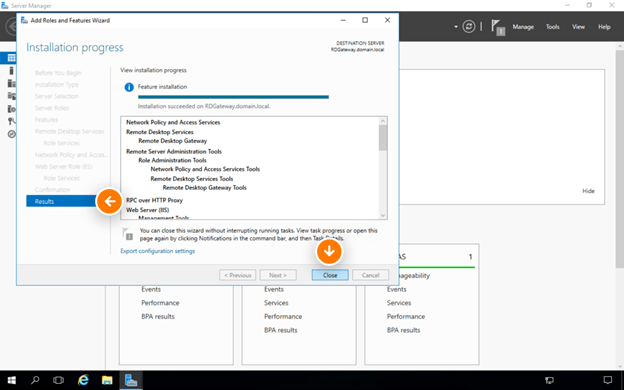
- Complete Installation
- Wait for the installation to finish, then click Close to exit the wizard.
Step 2: Configure Authorization Policies (CAP & RAP)
Authorization policies control which users can access the RD Gateway and the internal resources they are allowed to connect to.
1. Connection Authorization Policy (CAP)
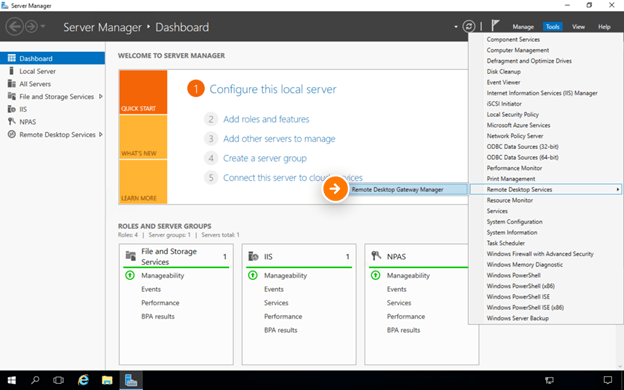
- Open RD Gateway Manager
- Navigate to Tools > Remote Desktop Gateway Manager in Server Manager.
- Access Policies
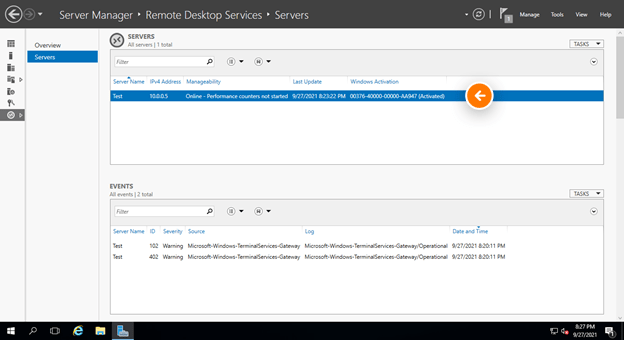
- In RD Gateway Manager, go to the left pane and expand Policies.
- Create a New CAP
- Right-click Connection Authorization Policies and select Create New Policy.
- Choose the Wizard option to simplify the setup process.

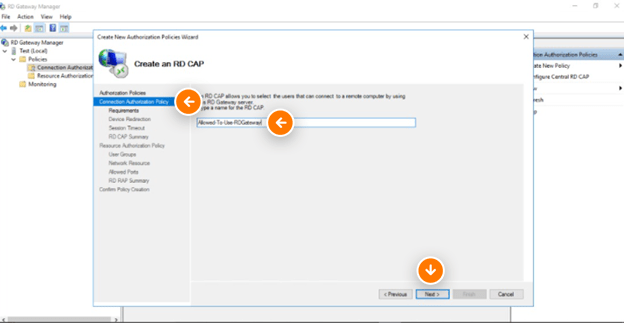
- Name the CAP
- Enter a descriptive name (e.g., “Allowed Users for RD Gateway").
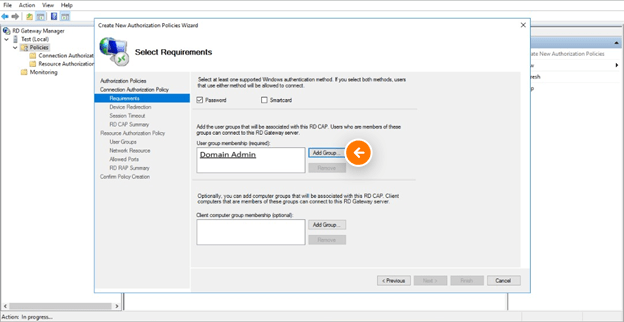
- Specify User Groups
- Add the Active Directory groups (e.g., Domain Admins) that are authorized to connect through the RD Gateway.
- Best practice: Create specific user groups for better control over access.
- Configure Device Redirection
- Accept the default settings for device redirection unless specific restrictions are required.

- Set Timeout Values
- Configure timeout settings for idle sessions as needed for your environment.

- Finalize the CAP
- Review and confirm your settings, then save the CAP configuration.
2. Resource Authorization Policy (RAP)
- Create a New RAP
- In the RD Gateway Manager, right-click Resource Authorization Policies and select Create New Policy.
- Use the Wizard for guided configuration.

- Name the RAP
- Enter a descriptive name (e.g., “Domain Controller Access").
- Add User Groups for Network Access
- Select the user groups that are allowed to access internal network resources through the RD Gateway.

- Specify Server Groups
- Identify the server groups or specific servers users can connect to.
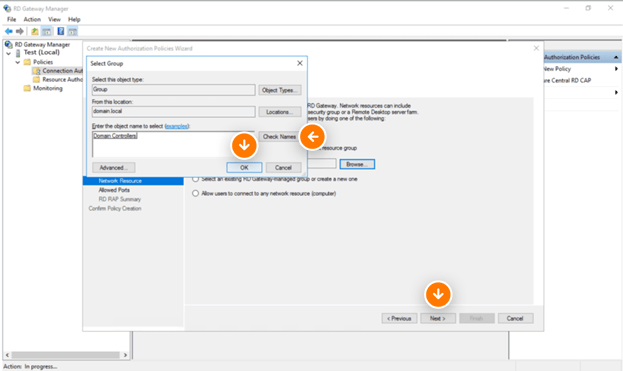
- Example: For this tutorial, use the Domain Controllers group.

- Verify Group Names
- Use the Check Name button to confirm that the group exists in Active Directory.
- Set RDP Port
- Specify the RDP port (default: 3389), or select Allow connections only to port 3389.

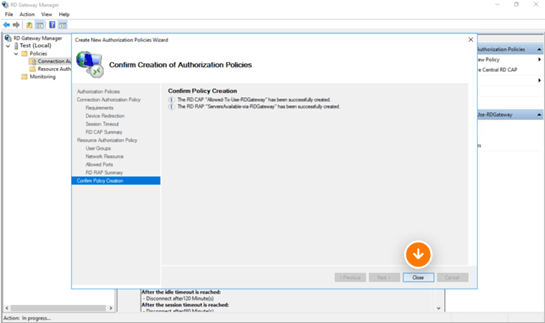
- Finalize the RAP
- Review and confirm your settings, then save the RAP configuration.
Step 3: Install an SSL Certificate
To secure connections, the RD Gateway must have a valid SSL certificate installed.
- Access Server Properties
- In the RD Gateway Manager, right-click your server name and select Properties.

- Import SSL Certificate
- Go to the SSL Certificate tab and select Import a certificate into the RD Gateway.

- Upload Certificate File
- Browse for the PFX file containing the certificate, then click Open.
- Enter Certificate Password
- Input the password for the PFX file to complete the import.
- Verify Installation
- Ensure the SSL certificate is successfully imported and bound to TCP port 443.
Note: While a self-signed certificate is used in this tutorial, a certificate from a trusted provider is strongly recommended for production environments.

Step 4: Test RD Gateway Connection
- Set Up a Remote Desktop Client
- Open the RDP client on a test machine and configure it to use the RD Gateway server’s FQDN.
- Test User Access
- Attempt to connect using credentials from an authorized user group.
- Verify Connectivity
- Ensure the client can access the internal servers specified in the RAP.

- Troubleshoot If Needed
- Check network connectivity, verify CAP and RAP settings, and confirm SSL certificate validity if issues occur.

Frequently Asked Questions about Remote Desktop Gateway
1. Can I use Remote Desktop Gateway with multiple Remote Desktop Servers?
Yes, you can configure RD Gateway to manage access to multiple Remote Desktop Servers.
By creating specific Resource Authorization Policies (RAPs), you can control which user groups have access to particular servers. This allows you to centralize and scale remote access efficiently, ensuring each user only connects to the resources they are authorized to access.
2. What are the system requirements for setting up a Remote Desktop Gateway?
To set up an RD Gateway, ensure your server meets the following minimum requirements:
- Operating System: Windows Server® 2012 or later.
- Hardware:
- At least 2 GB of RAM (more for larger setups).
- A dual-core processor or better.
- Adequate disk space for the operating system and roles.
- Network: A reliable network connection.
- SSL Certificate: A valid SSL certificate for secure communication.
These requirements may vary based on the number of users and the scope of your setup.
3. How do I troubleshoot connection issues with Remote Desktop Gateway?
If users encounter connection problems, follow these steps:
- Check Network Connectivity:
Ensure the RD Gateway server is reachable from the client device. Verify that firewalls or routing rules aren’t blocking traffic.
- Verify SSL Certificate:
Confirm that the SSL certificate is properly installed on the RD Gateway and trusted by client devices. Certificates should match the server’s fully qualified domain name (FQDN).
- Review CAP and RAP Configurations:
Ensure the user is part of a Connection Authorization Policy (CAP) group and has permissions under a Resource Authorization Policy (RAP).
- Inspect Event Logs:
Use the Event Viewer on the RD Gateway server to identify any errors related to RD Gateway services.
- Test RDP Port Accessibility:
Confirm that the default RDP port (3389) or any custom port is open and accessible on both the server and the client network.
How V2 Cloud Simplifies Remote Desktop Gateway Setup
Configuring a Remote Desktop Gateway can be time-intensive, requiring detailed setups for SSL certificates, policies, and server roles. V2 Cloud eliminates these complexities with a fully integrated virtual desktop solution that’s ready to use out of the box.
- Pre-Configured Infrastructure: V2 Cloud handles the heavy lifting by providing virtual desktops with built-in remote access capabilities. No need to manually configure RD Gateway roles or manage SSL certificates.
- Enhanced Security: With advanced encryption and multi-factor authentication, V2 Cloud ensures your remote connections are as secure as those created by RD Gateway, but with less effort.
- Scalability and Flexibility: Scale your resources up or down as needed, without the hassle of modifying policies or adding servers. V2 Cloud’s platform grows with your business, offering the ultimate flexibility.
- Simplified IT Management: Say goodbye to configuring roles, policies, and troubleshooting connection issues. V2 Cloud provides an intuitive interface that allows you to focus on your core business instead of IT maintenance.
Talk to a Cloud Expert Today and experience the power of secure, hassle-free remote access. Modernize your IT infrastructure and empower your team to work from anywhere!




