 A developer on your team asks to ditch the company Windows® laptop and work from Ubuntu at home. Your first thought is probably: is Linux safe enough for that?
Short answer: yes, Linux is safe for remote work when it’s patched, encrypted, and configured on purpose. The operating system blocks most of the drive-by malware that plagues Windows fleets. What it won’t do is protect you from an open SSH port, a kernel that’s three months behind, a poisoned package, or an employee who types their password into a fake login page.
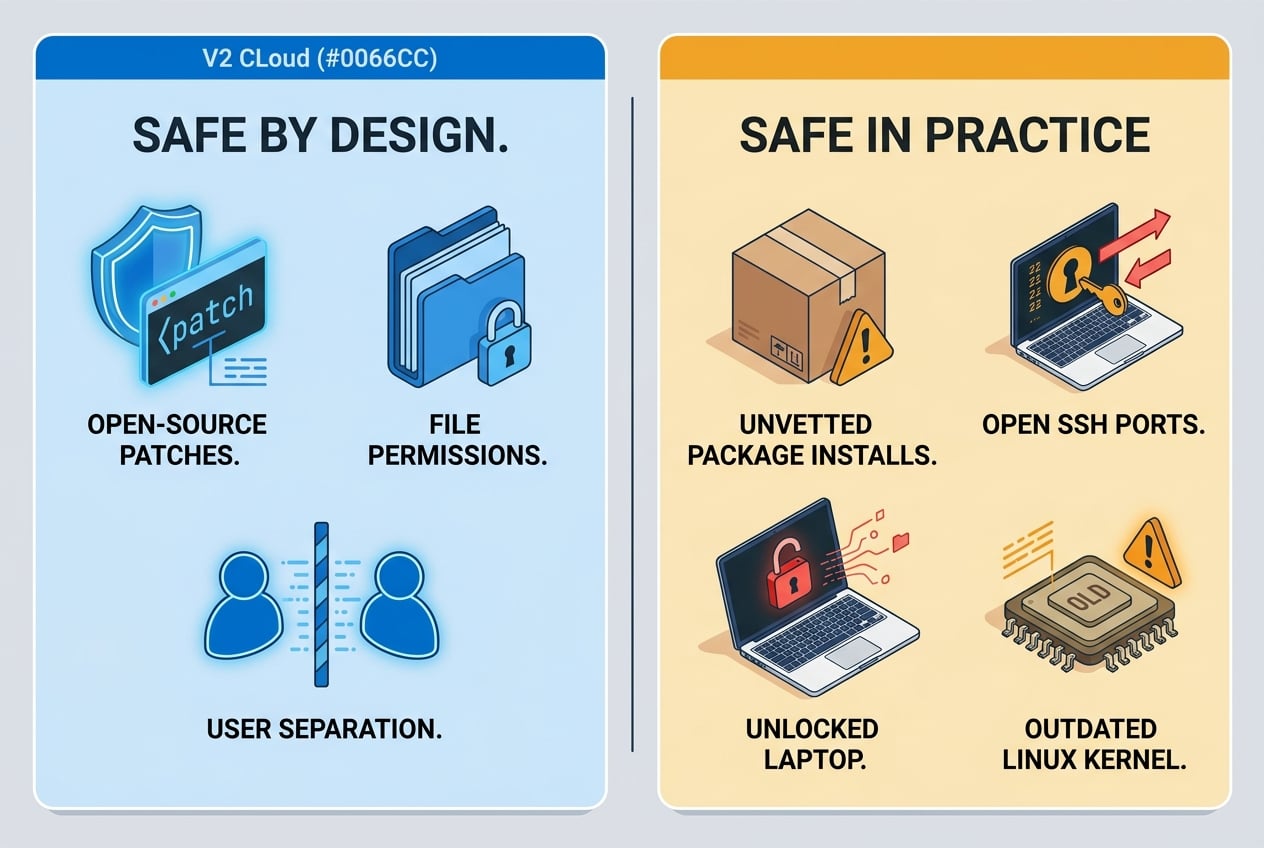
That gap is the whole story. Linux is safe by design. It is not safe by default once you hand it to someone working from a home network with no IT person in the room.
This guide covers the risks that actually hit remote Linux users in 2026, a hardening checklist you can hand to your team, and why more IT managers are moving Linux work off the laptop entirely.
Key Takeaways
- Linux resists most traditional malware, but that doesn’t make a remote Linux laptop safe by itself.
- Most Linux incidents start with SSH brute force, unpatched kernels, or compromised packages.
- Full-disk encryption, key-only SSH, and fast patching close the biggest gaps.
- Many security tools still cover Windows far better than Linux endpoints.
- A cloud-hosted Linux desktop keeps company data off the device altogether.
Is Linux Safe? The Short Answer
Linux is safe by design, not safe by default. Linux earns its reputation honestly. But the reputation was built on servers run by professionals, not laptops run by busy people at home.
What Linux Gets Right
Three things make Linux hard to infect casually. Downloaded files don’t execute until someone deliberately marks them executable. Regular users can’t write to system directories, so malware running without root hits a ceiling fast. And open source code means a disclosed flaw can be reproduced and patched quickly, often within hours (LinuxTeck, 2026).
The numbers back it up. Linux accounted for roughly 1.3% of global malware detections in 2025, despite running around 90% of public cloud workloads (CommandLinux, 2026).
Why “Linux Doesn’t Get Viruses" Is the Wrong Question
Nobody serious attacks Linux with a classic virus anymore. They don’t need to.
Elastic’s 2025 Global Threat Report, which counts Linux at about 9% of malware signature events (a different method than the 1.3% figure above), found that 89% of all endpoint behaviors logged on Linux systems were brute-force attempts, mostly against public-facing SSH (Swif, 2026). Attackers aren’t sneaking files onto Linux machines. They’re guessing passwords, exploiting unpatched services, and borrowing trust.
Linux stops malware files well. Most modern attacks on Linux don’t use malware files at all.
The Real Risks for a Remote Linux Worker in 2026
Here’s what actually goes wrong when Linux leaves the office.
Exposed SSH and Credential Spraying
Developers love SSH. So do bots. Automated scanners hit public IP addresses around the clock looking for SSH logins to guess (Comparitech).
On a remote setup, the danger usually comes from convenience. Someone forwards port 22 on their home router so they can reach their workstation from a café. Password login is still switched on. Now that machine is one weak password away from being someone else’s.
Patch Lag on a Kernel That Ships CVEs Daily
Linux kernel Common Vulnerabilities and Exposures (CVE) disclosures hit 3,529 in 2024 and 5,530 in 2025, roughly 8 to 9 new entries a day (CommandLinux, 2026). Part of that jump is administrative: the kernel team became its own CVE Numbering Authority in early 2024 and now logs far more fixes. Still, the volume is real.
And exploits matter. Mandiant’s M-Trends 2026 report found exploits were the leading initial infection vector in 2025, at 32% of breaches (Comparitech). A home laptop that postpones updates for “after this sprint" is carrying that risk every week.
Supply Chain and Package Risks
This one keeps security teams up at night. In 2024, the XZ Utils compression library was found carrying a backdoor planted by a patient contributor over roughly two years. It came close to shipping in mainstream distributions.
The lesson, as Swif puts it, is that the “many eyes" idea doesn’t scale to the hundreds of small, single-maintainer libraries modern distributions depend on (Swif, 2026). Developers make it worse by pulling packages from language registries directly. Kaspersky researchers found malicious Python packages on PyPI in early 2026 that targeted both Windows and Linux with a malware dropper (Kaspersky Securelist, Q1 2026).
Your OS choice doesn’t protect you from a bad pip install.
Lost Laptops and Unencrypted Disks
A stolen laptop is the least technical threat on this list. It’s also one of the most common.
Many Linux installs skip full-disk encryption because the installer made it optional and nobody ticked the box. Pull the drive out of that machine and every file, SSH key, and saved browser session is readable. No exploit required.
Phishing Doesn’t Care Which OS You Run
Credentials typed into a fake Microsoft 365® or Google login page work just as well for an attacker whether the victim ran Ubuntu or Windows. The browser is the attack surface, and it looks the same on every operating system.
If your team runs Linux on personal hardware, your company data is only as safe as the least patched laptop. We built our Linux VDI so that data stays in our data centers instead.
Is Your Team’s Linux Setup Actually Safe? A Hardening Checklist
You can make a remote Linux laptop genuinely safe. It just takes deliberate setup, and someone has to own it. Use this table as your baseline.
Most remote Linux risk comes from five gaps, and each has a well-known fix.
| Risk | Control | Who owns it | Effort |
| SSH brute force | Disable password login, use key-based auth, never expose port 22 directly | IT, enforced by config | Low |
| Patch lag | Automatic security updates, a maximum patch window (for example, 7 days) | IT policy, user reboots | Low |
| Poisoned packages | Prefer distro repositories, pin dependencies, review new packages | Engineering leads | Medium |
| Lost or stolen device | Full-disk encryption (LUKS), screen lock, remote wipe plan | IT at setup | Low at install, high after |
| Phishing | Multi-factor authentication (MFA) on every work account, training | IT and security | Medium |
| No visibility | Endpoint detection with real Linux support, centralized logs | Security | High |
A few notes from experience:
- Encryption is an install-time decision. Adding LUKS to an existing machine usually means a rebuild. Get it right on day one.
- Unattended upgrades handle packages, not reboots. A patched kernel does nothing until the machine restarts. Set a reboot expectation.
- Key-only SSH is not optional. If a machine must accept inbound SSH, put it behind a VPN or bastion host, never straight on the internet.
- Write down who owns each row. Checklists without owners become suggestions.
The Gap Most IT Teams Miss: Windows-Centric Security Tooling
Here’s the uncomfortable part. Even teams that harden Linux well often can’t see it.
Elastic’s 2025 report notes that endpoint detection and response (EDR) coverage for Linux lags badly behind Windows workstation coverage at most enterprises (Swif, 2026). Your device management tool might enforce BitLocker® on every Windows laptop and have nothing to say about the three Ubuntu machines in engineering.
So ask a blunt question: if one of your remote Linux laptops were compromised tonight, how would you find out?
If the honest answer is “we probably wouldn’t," the laptop isn’t safe, no matter how solid the OS is. An unmonitored Linux laptop is safe right up until the day it isn’t, and you won’t know which day that was.
Local Linux Laptop vs. Cloud-Hosted Linux Desktop
Everything above assumes the work happens on the laptop. That’s the assumption worth challenging.
When your team works on a cloud-hosted Linux desktop, the laptop becomes a window, not a vault. Source code, credentials, and customer data live on infrastructure you control. The device at home just displays the session.
That shifts the risk picture significantly.
Moving Linux work to the cloud removes the device from most of the risk equation.
| Factor | Local Linux laptop | Cloud-hosted Linux desktop |
| Where company data lives | On the device’s disk | In the data center |
| Stolen laptop impact | Potential data breach if unencrypted | Revoke access; data never left the server |
| Consistency across the team | Depends on each person’s setup | Same environment for everyone |
| Backups | Up to the user, often missing | Handled centrally |
| Access control | Local accounts per machine | Central login with MFA and SSO |
| Personal devices (BYOD) | Company data mixes with personal files | Company data stays separate |
This is exactly the problem we set out to solve. Our Linux VM gives your team a full Ubuntu desktop hosted in our data centers, reachable from any device with an internet connection. We back up every desktop daily, support MFA and SSO on login, and deploy new desktops in under 20 minutes, so onboarding a new developer doesn’t mean imaging another laptop.
It also makes BYOD and remote work far less nerve-wracking. A contractor can use their own machine without your repository ever touching their disk. When the contract ends, you remove their access and you’re done. No device to recover.
To be fair, a cloud desktop doesn’t make security somebody else’s problem. You still need strong passwords, MFA switched on, and sensible package habits inside the desktop. But you’re securing one controlled environment instead of 15 home laptops on 15 home networks. For most small IT teams, that trade is the difference between a manageable job and an impossible one. You can read more about how we protect that environment on our security and compliance page.
Want a Linux environment your team can reach from anywhere without company data landing on their laptops? Our cloud experts can walk you through a setup built around your tools.
Is Linux Safe Frequently Asked Questions
Is Linux safe to use for work?
Yes. Linux is safe for work when it’s kept patched, uses full-disk encryption, and has MFA on the accounts that matter. The main risks are exposed SSH, patch delays, and compromised packages rather than traditional viruses.
Do I need antivirus on a Linux laptop?
Classic antivirus matters less on Linux than on Windows, but monitoring still matters. For a work machine, endpoint detection with real Linux support is more useful than signature scanning, because most Linux attacks don’t rely on malware files.
Is Ubuntu safe for remote work?
Ubuntu is a solid choice for remote work, with regular security updates and wide software support. Turn on disk encryption at install, enable automatic security updates, and keep SSH closed to the internet. If you’d rather not manage it on every laptop, we offer cloud-hosted Ubuntu desktops.
Can Linux get ransomware?
Yes. Linux ransomware attacks rose 62% between 2022 and 2023, with virtualization servers a favorite target (CommandLinux, 2026). Desktop users are hit less often, but backups and patching are still your best defense.
Is it safe to install software from outside my distro’s repositories?
It’s riskier. Distribution repositories are reviewed and signed, while language registries like PyPI and npm have hosted malicious packages. Pin versions, check who maintains a package, and avoid running install scripts you haven’t read.
Is a cloud-hosted Linux desktop safer than a local install?
For most remote teams, yes. Company data stays in the data center instead of on the laptop, so a lost device doesn’t become a data breach. You also manage one consistent environment instead of every employee’s personal setup. Our secure remote access setup is built around that model.


