
As of recent years, if you are assessing the security of Remote Desktop Protocol (RDP) connections, there are several updated considerations you should be aware of.
So, is RDP encrypted? The short answer is yes, but the standard levels of encryption can vary based on the security settings used and the versions of the clients involved. In addition to SSL/TLS encryption, advanced protections like Network Level Authentication (NLA) significantly enhance security by pre-validating users before establishing connections.
This article will dive deeper into the RDP security layer and how organizations seeking higher security options can leverage this solution.
Remote Desktop Protocol (RDP) is a technology developed by Microsoft that provides users with a graphical interface to connect to another computer over a network connection. Introduced as an add-on called Windows Terminal Server with Windows NT Server 4.0 in 1998, RDP has been included in all subsequent Windows operating systems starting with Windows XP in October 2001.
RDP enables remote users to experience a full desktop environment—complete with sound, clipboard integration, printer access, and high-resolution graphics that the remote desktop host can adjust based on available bandwidth.
Over the past two decades, RDP has evolved through multiple versions, enhancing functionality and reliability as a core tool for remote access. Yet, it has also faced significant security challenges, particularly with the rise of remote work, increased cloud reliance, and the broader use of distributed computing environments.
RDP’s flexibility has unfortunately made it a target for misuse in cyberattacks, including ransomware, with numerous threat and breach reports highlighting vulnerabilities in the last few years.
RDP is versatile, supporting a wide range of applications regardless of organizational size:
These use cases have become increasingly crucial in today’s “work-from-anywhere" culture, though certain applications pose higher security risks and require stringent controls to mitigate potential threats.

RDP’s vulnerabilities are inherently linked to the protocol’s design, which allows direct connection to remote computers. This capability, while useful for legitimate remote access, also opens up significant security risks if not properly managed.
Once attackers establish a connection through RDP, they can potentially gain unrestricted access to the system and network, leading to widespread security breaches. Here are some common vulnerabilities and exploits to watch for:
Windows Remote Desktop employs an encrypted channel to safeguard remote desktop sessions from eavesdroppers within your network. However, it’s important to note that earlier versions of RDP have limitations in their encryption methods, which could expose them to man-in-the-middle attacks, allowing unauthorized access without permission.
From Windows Vista onwards, including Windows 7, 8, 10, and server versions like Windows Server 2003/2008/2012/2016, RDP supports encryption through SSL/TLS, enhancing security significantly. However, Microsoft has discontinued support for some of these older systems, which means they no longer receive security updates and do not meet modern security standards.
While RDP offers more robust security features than some alternatives, like VNC, which does not encrypt entire sessions, vulnerabilities still exist. For example, granting remote administrative access increases the risk of unauthorized system access.
Yes, RDP is encrypted, but it has significant caveats to consider.
Most modern RDP systems and services, including V2 Cloud, enable encrypted connections by default. Nonetheless, older versions of RDP software may not support the highest current encryption standards, posing security risks, especially in environments with legacy systems.
To maximize security in your remote desktop environment, it’s crucial to audit all client devices across your network and upgrade them to support the highest level of encryption available. As part of this process, organizations often run an external vulnerability scan to identify exposed ports or outdated protocols that attackers could exploit. You also have the option to customize encryption levels through settings in Microsoft’s RDP or choose from various third-party remote desktop solutions that offer higher encryption standards.
In essence, maintaining a secure RDP setup requires regular updates, careful management of user permissions, and potentially supplementing Microsoft’s built-in tools with more secure third-party solutions to cater to your specific security needs.
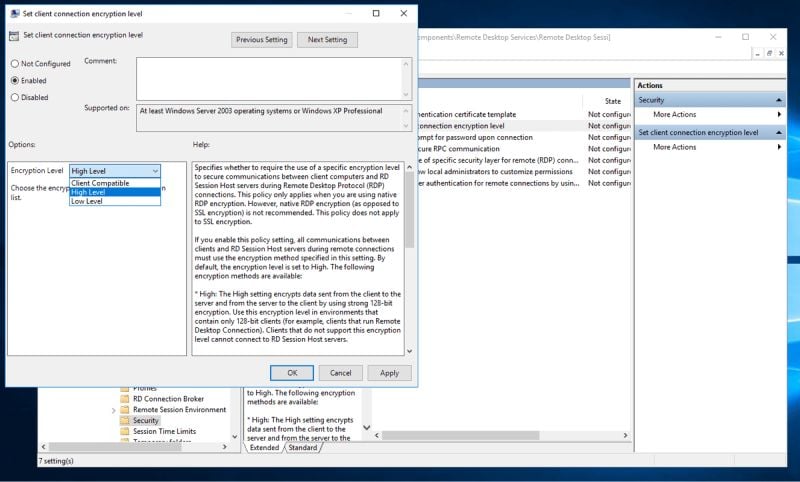
Remote Desktop Protocol while powerful, presents significant security risks if your remote desktop services are not properly secured beyond its default settings. Here’s a guide to fortifying RDP within your organization:
RDP benefits from being integrated within the Microsoft ecosystem, which means it regularly receives updates directly through Microsoft’s standard patch cycle. It is critical to enable and monitor these updates to ensure both client and server software remain protected against the latest vulnerabilities.
Make sure all platforms running Remote Desktop clients are kept up-to-date, as older versions may lack support for the latest encryption standards and other security features.
To significantly enhance security, implement two-factor authentication. This could involve using hardware tokens like YubiKey, software tokens, or smartcards that utilize certificates.
2FA adds a critical second layer of defense that can protect against compromised credentials.
Use both software and hardware firewalls to restrict access to RDP-specific ports (default TCP 3389). Limiting these ports can help mitigate unauthorized access attempts and reduce the risk of brute-force attacks.
Employing an RDP gateway can further secure access, particularly for connections originating from outside the network. Consider integrating with VPN solutions to control access to remote connections through secure and encrypted channels.
NLA should be enabled by default on newer Windows systems like Windows 10 and Windows Server 2012 R2/2016/2019. This feature adds an extra layer of security by requiring authentication before establishing an RDP session, thus preventing unauthorized access attempts before they reach the server.
Verify and enforce NLA through Group Policy settings, ensuring all your remote desktop network connections meet your security standards.
By following these best practices, organizations can significantly reduce the risks associated with RDP and ensure a secure remote desktop environment. These measures are essential not just for compliance with security standards but also for safeguarding sensitive organizational data and systems from potential cyber threats.
When it comes to securing remote access to a network, the choice between RDP and Virtual Private Network (VPN) involves considering the specific security needs and setup of an organization. Both technologies serve critical roles in network management and remote access but offer different levels of security and functionality.
RDP allows users to take control of a remote computer or virtual machine over a network connection, providing a graphical interface for managing another computer from a distance. However, RDP, when exposed directly to the internet without additional protections, can become a significant vulnerability.
VPN, on the other hand, creates a secure, encrypted tunnel between a device and a network. This tunnel ensures that data transmitted remains private and secure, making it harder for unauthorized parties to intercept or eavesdrop on communications. The VPN acts as if the device is directly connected to the internal network, securely providing access to network resources.
For most businesses that need to provide remote access to their internal networks, using a VPN to secure the connection, supplemented by RDP for remote desktop access when needed, offers a robust security setup.
This approach protects against a wide array of security threats while maintaining the functionality required for effective remote work.
When it comes to remote desktop solutions, V2 Cloud’s Virtual Desktop Infrastructure (VDI) stands out as a more secure and reliable alternative to traditional RDP.
Here’s a closer look at the security features that make V2 Cloud’s VDI an excellent choice for businesses prioritizing data security:
Our data centers are designed for maximum reliability, boasting a 99.95% service level agreement. They feature fully redundant fiber networks and power supplies, gated entries with restricted and logged staff access, and continuous video surveillance. These facilities comply with rigorous SOC, PCI, and HIPAA standards, undergoing periodic security audits to ensure the highest level of data protection.
V2 Cloud utilizes the latest hypervisor updates to run each virtual machine, protected by comprehensive UFW firewalls. Data redundancy is guaranteed with RAID-1 replication using NVMe drives, ensuring high performance and reliability.
Each virtual machine operates within a private network, isolated remote desktop connections, and is secured without incoming ports, enhancing security against external threats. Clients can customize their firewall settings and manage private network configurations via our user-friendly management console. Additionally, our public IPs are fortified against DDoS attacks, and we employ IPsec VPNs for secure connections to office resources.
Secure connections to cloud desktops are facilitated via SSL HTTPS through both the app and web interfaces. RDP over SSH tunneling is used for connections made through the desktop app, which supports SAML integration and multi-factor authentication. A security lockout mechanism monitors for and responds to multiple failed login attempts, safeguarding remote desktops against unauthorized access.
V2 Cloud offers daily snapshot backups with a 7-day retention policy as part of our business plan. These backups are stored offsite in a secondary location to protect against ransomware attacks and enable quick recovery in case of disaster or accidental data deletion.
Each business plan includes Malwarebytes Pro, providing top-tier antimalware protection with real-time monitoring and nightly scans to ensure your virtual environment remains secure against the latest threats.
For businesses looking to enhance their remote desktop capabilities while maintaining rigorous security standards, V2 Cloud’s VDI offers a comprehensive and secure solution.
Discover more about V2 Cloud and start securing your remote operations today.

Your V2 CloudCare team — real people, on the line.


